What might the next person find after you finish using a public computer? Signing out is important, but depending on the workstation’s configuration, downloads, saved credentials, browser data, or open sessions may still need attention. Public computer security best practices therefore involve more than one final click: users need reliable session habits, and administrators need safeguards that keep shared workstations consistent.
It’s reasonable to want quick, convenient access without leaving personal information behind or changing the experience for the next user. This checklist covers what to do before signing in, while using a shared computer, and when you finish. It also separates steps individuals can take from controls administrators should manage, including updates, access restrictions, and workstation recovery.
Reboot-to-restore software can return a shared computer to a clean baseline on restart, complementing rather than replacing privacy practices, antivirus, and access controls. The result is a practical routine for protecting personal information while supporting a dependable workstation for each successive session.
Key Takeaways
- Use a before, during, and after routine to reduce the chance of leaving personal information or an active account behind.
- Apply public computer security best practices by pairing user habits with administrator controls, rather than relying on private browsing alone.
- Choose a personal device for sensitive tasks such as banking, health portals, and entering payment details.
- Help keep shared workstations dependable with a maintained baseline, restricted changes, endpoint monitoring, and consistent recovery procedures.
- Understand how reboot-based restoration can clear session changes when a workstation restarts, while remaining one layer of a broader security approach.
Public Computer Security Best Practices: What Users and Administrators Need to Protect
Public computer security means protecting people, accounts, information, and the workstation itself, including the condition it’s left in for the next session. The same principles apply in libraries, schools, community spaces, and shared organizational terminals. A useful checklist addresses both sides of shared access: what each person does during a session and how the organization maintains the computer between users.
These risks are connected, but they aren’t identical. Device security concerns the workstation’s software and settings. Account security concerns credentials and active sign-ins. Network security concerns how data travels between the computer and online services. Physical privacy includes people nearby who may see a screen or keyboard. Knowing which risk you’re addressing helps you choose a relevant safeguard instead of expecting one measure to solve every problem.
What makes a public computer different from a personal device?
With a personal device, you usually have more control over installed software, settings, and updates. On a shared workstation, those decisions typically belong to the organization, and users may not know how the computer is configured. Shared access also isn’t the same as public Wi-Fi: a public computer may connect through different kinds of networks, so don’t assume its connection is open or secure based on the location alone.
One session can leave changes for the next person. A downloaded file, altered setting, or browser session that remains open may affect privacy or the workstation’s condition. Phishing and unsafe downloads are examples of broader Internet security threats; removable media can introduce additional risks. These are reasons to use layered safeguards, not proof that every shared computer is compromised.
Who should use this public computer security checklist?
This checklist is for occasional users completing a brief task and for IT or library staff responsible for reliable access and endpoint condition. Users can reduce exposure through careful choices during a session. Administrators can manage settings, software, access, and recovery processes across workstations. Neither role replaces the other.
“User privacy habits protect the session; administrator device controls protect the shared workstation between sessions.” This distinction is central to effective public computer security best practices. Signing out matters, but it can’t substitute for device controls. Likewise, workstation recovery can’t protect an account if a user shares credentials. The practices in this guide reduce exposure, but no checklist can guarantee a risk-free session.
How Public Computer Risks Persist Beyond a Single Browsing Session
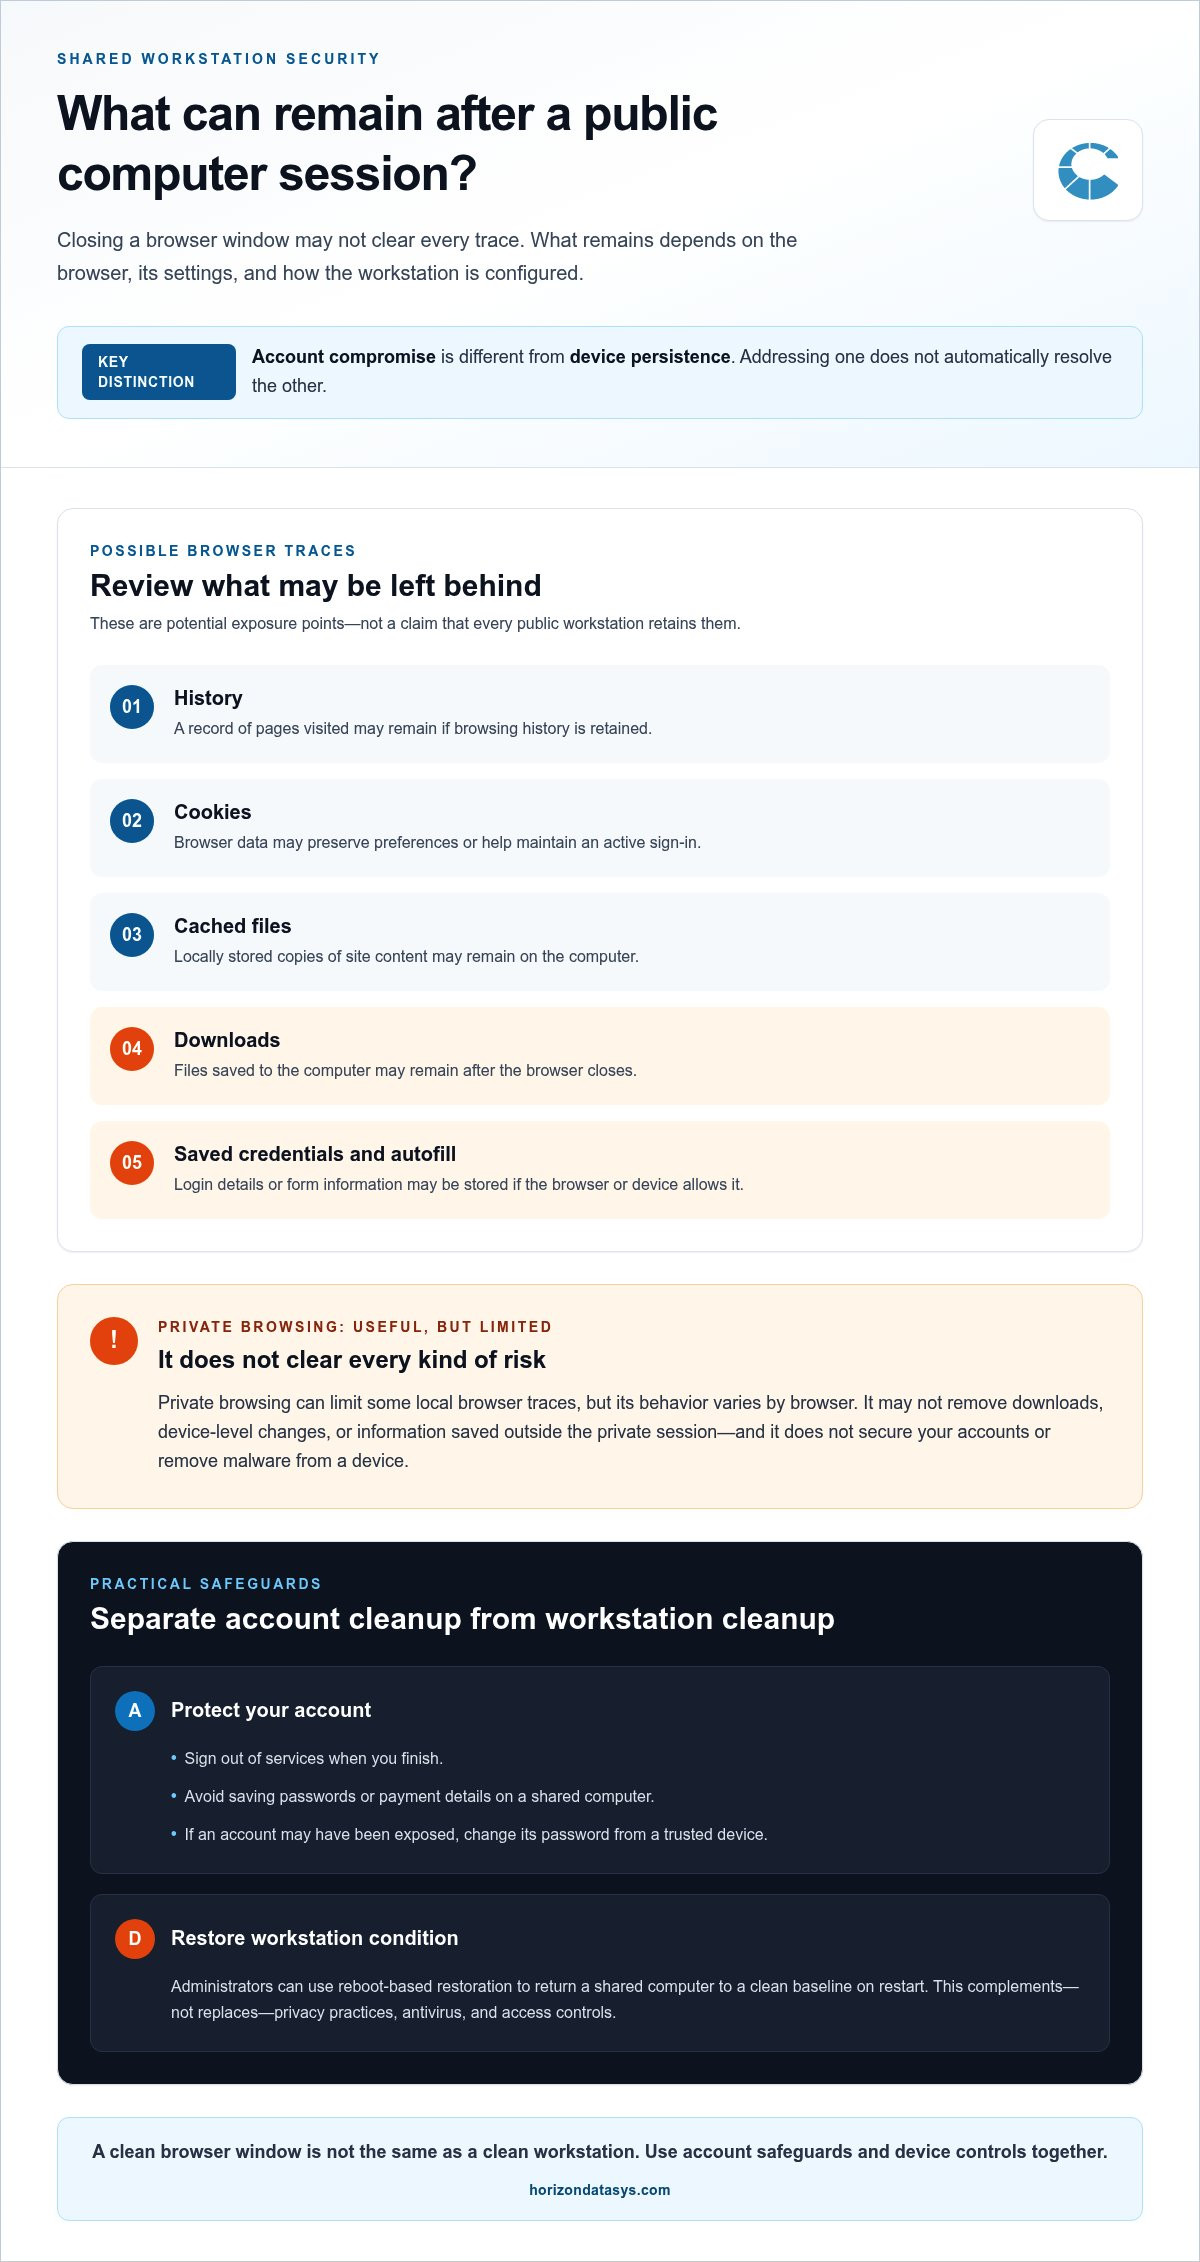
Closing a browser window doesn’t necessarily close every account session or remove every trace from a shared workstation. Two kinds of risk matter: account compromise, where someone gains access to an online account, and device persistence, where files or settings remain on the computer. Addressing one doesn’t automatically resolve the other.
What information can remain after a public computer session?
What remains depends on the browser, its settings, and how the workstation is configured. Potential exposure points include:
- History: a record of pages visited, if browsing history is retained.
- Cookies: small pieces of browser data that may preserve preferences or help maintain an active sign-in.
- Cached files: locally stored copies of site content that can help pages load faster.
- Downloads: files saved to the computer, which may remain after the browser closes.
- Saved credentials and autofill: login details or form information, if the browser or device allows them to be stored.
These are possibilities, not a claim that every public workstation retains this information. Private browsing can limit some local browser traces, but its behavior varies by browser. It may not remove downloads, device-level changes, or information saved outside the private session. “Private browsing limits local traces, but it doesn’t secure your accounts or remove malware from a device.”
How can an unsafe session affect the next user?
A downloaded file may remain in a shared folder. An unwanted extension or changed browser setting may carry into another session if the workstation allows those changes to persist. Phishing can trick someone into revealing credentials, while unsafe downloads or removable media can introduce malicious software. These risks don’t mean every public computer is infected, but ordinary browser cleanup shouldn’t be mistaken for a device security check.
To reduce account exposure, sign out of services and avoid saving passwords or payment details on a shared computer. General Cybersecurity best practices also reinforce the value of protecting credentials and staying alert to suspicious messages. If an account may have been exposed, changing its password from a trusted device addresses the account risk. Cleaning up the public workstation is a separate task.
Administrators can use reboot-based restoration to return a shared computer to a clean baseline on restart. Reboot Restore provides this endpoint recovery layer, while Reboot Restore Enterprise adds centralized management for network environments. Restoration can help discard session changes, but it doesn’t secure user accounts or replace access controls, antivirus, and other security measures.
Public Computer Security Layers: User Habits Versus Workstation Controls
Public computer security works best when responsibilities are clear. Users make safer choices during a session, while administrators manage the device’s configuration and condition across sessions. Private browsing can reduce some browser traces, but it doesn’t make an untrusted workstation safe for sensitive activity or protect an account if credentials are exposed.
Layer
Actions and purpose
Limitations
User actions
Choose lower-risk tasks, protect credentials, avoid unnecessary downloads, sign out of accounts, and shield the screen from nearby viewers. These habits reduce session and privacy exposure.
Users can’t independently verify every device setting, update, or security control. A private window or VPN doesn’t make a compromised workstation trustworthy.
Administrator controls
Keep operating systems supported and updated, apply least-privilege permissions, monitor endpoints with security tools, and configure session reset controls. These measures reduce vulnerabilities and limit persistent changes.
No single control prevents every threat. Updates, endpoint protection, access controls, and restoration address different parts of the risk.
What can users control during their session?
Start by choosing what to do on the shared device. For banking, health portals, payments, or other sensitive tasks, use a personal device when possible. If a public computer is necessary, don’t save credentials, avoid downloads unless essential, sign out of each service rather than merely closing its tab, and keep private information out of view. These public computer security best practices lower exposure, but they can’t confirm the device’s security state.
What should administrators control across shared workstations?
Administrators establish a dependable baseline: maintain supported operating systems, install updates, restrict standard-user permissions, and review endpoint security signals. Least privilege limits what an ordinary session can change. Monitoring helps identify suspicious activity. These safeguards work together, but none should replace the others.
Restore-on-restart controls add another layer by returning a configured workstation to its baseline when it restarts. Reboot Restore provides this approach for shared computers, and Reboot Restore Enterprise adds centralized management for network environments. Learn more in this reboot-to-restore software explainer.
Endpoint recovery restores workstation state; it isn’t a backup, antivirus, or identity-protection control. A reset may discard session changes, but it doesn’t secure exposed credentials or replace endpoint protection and access controls. A layered design gives each safeguard a specific job.
A Before, During, and After Checklist for Using a Public Computer
A consistent routine makes it easier to protect personal information without assuming that any single step makes a shared workstation completely safe. For banking, health portals, payment details, and other sensitive activity, use a personal device whenever possible. If you need to use a public computer, follow the facility’s instructions and work through these steps in order.
Before and during your session
- Choose the right device for the task. If the activity involves sensitive account or payment information, consider whether it can wait until you’re using a personal device.
- Check your surroundings. Before entering credentials, look for people who might see your screen or keyboard. Position the display to limit casual viewing, and don’t leave the workstation unattended while signed in.
- Use accounts carefully. Don’t save passwords, enable autofill, or leave recovery codes where someone else could access them. Use multifactor authentication when available, but keep backup codes private and don’t store them on the shared computer.
- Limit what you open or download. Avoid downloading sensitive files or installing software. If a task requires a file, follow the institution’s rules for handling it and remove it only if permitted.
How should you leave a public computer safely?
- Sign out of each account. Use each service’s sign-out option, then close private windows. Closing a tab alone may leave an account session active.
- Review local activity. Clear browser data if appropriate and allowed, and check for personal files you’re permitted to remove. Don’t connect personal USB storage unless the task requires it and the facility allows it.
- Finish according to the facility’s instructions. Follow on-screen or posted directions for ending the session or shutting down. Report suspicious pop-ups, unexpected changes, or unusual device behavior to staff rather than trying to repair the workstation yourself.
These public computer security best practices reduce common points of exposure, but they can’t verify the workstation’s security or guarantee that an account is protected. If you suspect you entered credentials into a questionable session, use a trusted device to review the account and take appropriate steps, such as changing its password.
For organizations, a consistent workstation baseline can complement these user habits. Learn how Reboot Restore for shared workstations can help return a computer to its configured baseline after restart.
How Organizations Keep Public Workstations Consistent Between Users
Reliable public computer security best practices depend on an operating routine, not a single cleanup step. A defined workstation baseline gives staff a known starting point, while restricted permissions and endpoint monitoring help preserve that state and surface unexpected activity. Recovery controls can then help return computers to the intended configuration between sessions.
What belongs in a shared workstation security routine?
Document what “ready for use” means for each workstation, then maintain that state consistently. A practical routine should cover:
- Approved software: Keep only the applications and browser extensions required for the workstation’s intended use.
- Operating-system maintenance: Use a supported operating system and apply updates through a planned process.
- Restricted permissions: Limit user access so routine sessions can’t make unnecessary system-level changes.
- Session procedures: Provide clear instructions for starting and ending a session, reporting suspicious behavior, and handling unexpected prompts or device changes.
- Monitoring and response: Review endpoint security signals and establish how staff should escalate concerns. If a computer behaves unexpectedly, follow the organization’s response procedure instead of returning it to service without review.
Test maintenance and recovery procedures in a controlled way, and document the results. The right schedule and configuration depend on how each environment uses its workstations. A library computer and a shared terminal in an organization may have different operational needs.
When does reboot-to-restore fit public computer security?
Reboot-based restoration is useful when routine sessions may leave changes behind and the organization wants a repeatable way to return a shared computer to its configured baseline. Reboot Restore automatically restores shared computers to a clean baseline on restart. Reboot Restore Enterprise adds centralized management for network environments, supporting consistent administration across connected workstations.
Restoration is one layer, not a substitute for maintaining the baseline. It complements, rather than replaces, operating-system patching, endpoint protection, backups, and access controls. It also doesn’t protect user accounts or guarantee that a threat has been detected. Those responsibilities require their own safeguards and procedures.
For planning considerations, see the Reboot Restore Enterprise evaluation guide. To explore centralized workstation restoration, Explore Reboot Restore Enterprise.
Build a Safer, More Consistent Shared-Computer Routine
Effective public computer security best practices combine the actions users take during a session with safeguards administrators maintain between sessions. Signing out, protecting credentials, and limiting sensitive activity can reduce personal exposure. Supported software, restricted permissions, endpoint monitoring, and clear procedures help maintain workstation integrity.
For organizations, consistency matters. Reboot Restore returns shared computers to a clean baseline state upon restart, helping discard session changes. Reboot Restore Enterprise adds centralized management for network environments. These recovery capabilities complement essential controls such as patching, endpoint protection, backups, and access management. They don’t replace them.
A clear routine gives users practical steps to follow and gives IT teams a dependable framework for maintaining shared devices. To see how centralized restoration can support your environment, Explore Reboot Restore Enterprise. Layered safeguards and repeatable habits can make public access more predictable for both users and staff.
Frequently Asked Questions
Is it safe to use a public computer for online banking?
It’s safer to use a personal, updated device for online banking rather than a public computer. If you have no alternative, check the website address carefully, don’t save credentials or payment details, use multifactor authentication if available, and sign out when finished. Avoid proceeding if the computer behaves unexpectedly or prompts you to install unfamiliar software. These steps reduce exposure, but they can’t verify that a shared workstation is free of threats.
Can private browsing protect me on a public computer?
No. Private browsing can limit some browser history and other local traces, depending on the browser, but it doesn’t make the computer trustworthy. It won’t necessarily remove downloaded files or changes outside the private window, and it can’t stop someone from capturing credentials on a compromised device. Don’t treat a private window or VPN as a substitute for careful account use. Avoid sensitive activity on a device whose security you can’t verify.
What should I do after using a public computer?
Sign out of every account using each service’s sign-out option, then close private windows. Don’t rely on closing a tab. Clear browser data if appropriate and permitted, and remove personal files only when the facility allows it. Follow on-screen or posted shutdown instructions, and report suspicious behavior to staff. If you think you exposed a password, use a trusted device to review the account and change the password as needed.
Can malware remain on a public computer after a user logs out?
Yes. Logging out closes an account session, but it doesn’t necessarily remove software or system changes from the workstation. Depending on the device’s configuration, unwanted files, browser extensions, or malicious software could remain. Users generally can’t confirm the computer’s condition themselves, so report unusual behavior to staff. Administrators can use endpoint security controls and recovery procedures to assess and restore workstations, but no single step should be treated as complete protection.
Should I plug a USB drive into a public computer?
Avoid connecting personal USB storage unless you need it and the institution permits it. Removable drives can transfer files between devices, so they may introduce or carry unwanted content. If you must use one, follow the facility’s rules, avoid opening unexpected files, and don’t leave personal documents on the shared computer. For sensitive information, consider whether another transfer method or a personal device is more appropriate.
How can a library or school reset public computers between users?
Libraries and schools can establish a consistent workstation baseline, restrict user permissions, maintain supported software, apply updates, and document session procedures. Reboot-to-restore software can return a shared computer to its configured baseline when it restarts. Reboot Restore Enterprise adds centralized management for network environments. These public computer security best practices support consistent device condition, but should complement endpoint protection, patching, backups, and access controls.
Does reboot-to-restore software replace antivirus or backups?
No. Reboot-to-restore software helps restore a workstation’s configured baseline on restart, while antivirus detects and helps respond to threats, and backups preserve data for recovery. Access controls protect who can use accounts and systems. Each serves a different purpose. Reboot Restore can help discard session changes on shared computers, but it doesn’t secure exposed credentials or replace endpoint protection, backups, or identity safeguards.