What if the best way to prevent unauthorized software installation isn’t a single block, but a set of controls that still lets approved work move forward? Unapproved apps can create configuration drift and add support work, especially when users have installation rights they don’t need. At the same time, controls that interfere with essential updates can cause problems of their own.
The goal is a proportionate plan: limit who can install software, define which applications are approved, and make legitimate deployment and updates predictable. This article explains how to build that plan on Windows, including where application-control policies fit and how to choose controls for your devices and users.
You’ll also learn how to plan for changes that preventive controls miss. Reboot Restore can return shared computers to a configured baseline on restart, while RollBack Rx supports system recovery through snapshots. These tools complement policy controls, but they aren’t application allowlisting tools. Used for their distinct purposes, prevention and recovery can help keep Windows endpoints consistent without making routine work unnecessarily difficult.
Key Takeaways
- To prevent unauthorized software installation, match Windows controls to device roles and user needs rather than relying on one restrictive setting.
- Map essential applications, installers, update processes, and user groups before setting rules. This helps reduce disruption to approved workflows.
- Understand how account restrictions, application control, deployment, monitoring, and rollback differ so each control has a clear purpose.
- Roll out controls in stages, beginning with a pilot and continuing with monitoring and policy review, to spot issues before broad enforcement.
- If an unapproved change gets through, assess and contain it, remove it through approved processes, validate the system, and refine controls. Recovery tools can help restore system state but don’t replace prevention.
Why preventing unauthorized software installation takes more than removing admin rights
Removing local administrator rights is a useful first step, but it doesn’t answer every question: which software is approved, how should legitimate requests be handled, and what happens if an application still gets installed? Without clear answers, users can face unnecessary roadblocks while IT teams deal with inconsistent devices, avoidable support requests, unclear licensing records, and additional endpoint security concerns.
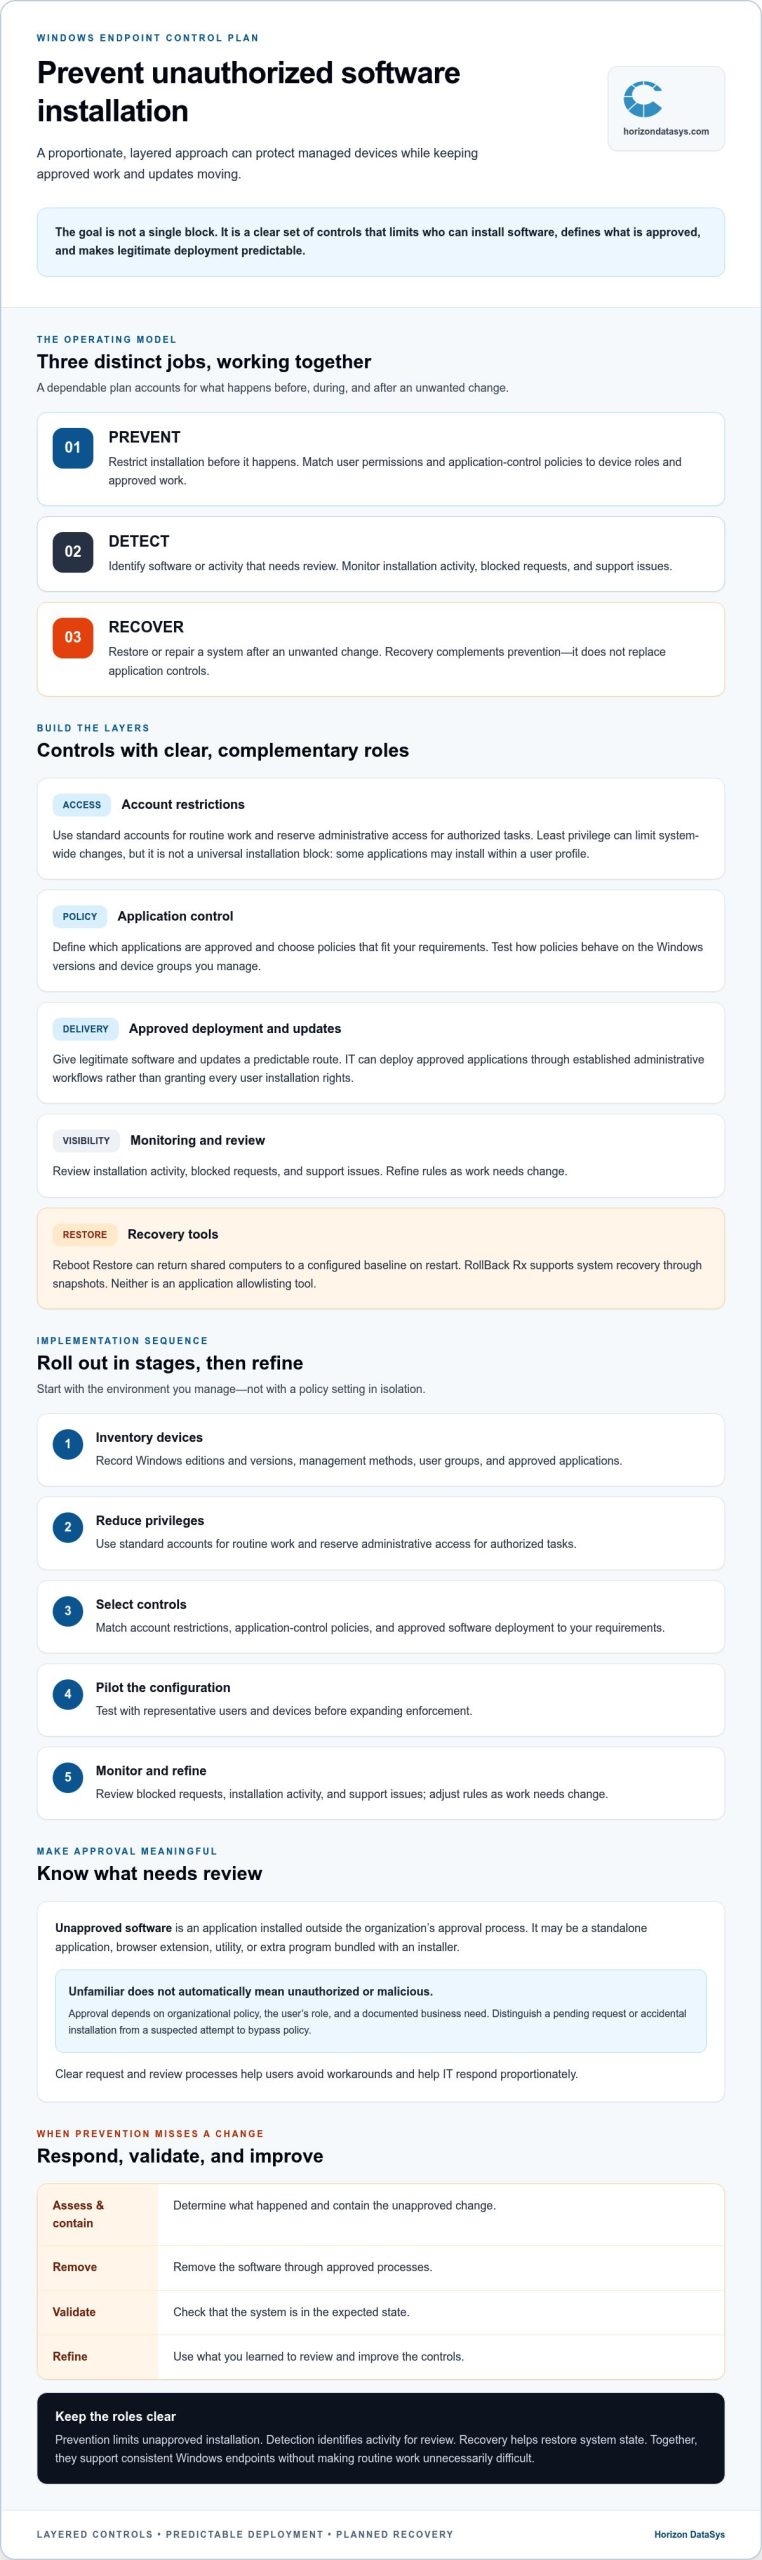
Unauthorized software installation is the installation of an application outside an organization’s approval process. Prevention restricts installation before it happens. Detection identifies software or activity that needs review. Recovery restores or repairs a system after an unwanted change. These functions are related but distinct, so a dependable plan accounts for all three.
What counts as unapproved software on a managed Windows device?
Unapproved software can include a standalone application, a browser extension, a utility, or an extra program bundled with an installer. But unfamiliar doesn’t automatically mean unauthorized or malicious. Approval depends on organizational policy, the user’s role, and a documented business need. An employee’s requested tool may be legitimate but still awaiting review, while a deliberate attempt to bypass policy calls for a different response than an accidental installation.
This distinction helps IT respond proportionately: review pending requests, assess accidental installs, and investigate suspected policy bypasses under established procedures. It also gives staff a clear way to request software instead of encouraging workarounds.
Why standard user accounts are a starting point, not a complete plan
Least privilege means giving each person only the permissions needed for their work. Applying the Principle of Least Privilege helps limit who can make system-wide changes, reducing opportunities to alter shared settings or install software that requires elevated access.
A standard account isn’t a universal installation block. Some applications may install within a user’s profile or behave differently depending on their installer and configuration. Windows edition, policy settings, and deployment methods also affect what users can do. Test common installers and application behaviors on your organization’s devices before relying on account restrictions alone.
To prevent unauthorized software installation reliably, pair appropriate user permissions with controls that reflect approved applications and business workflows. The next step is to assess the available Windows controls and decide how they should work together.
How to block unapproved software with layered Windows controls
A practical control plan starts with the environment, not a policy setting. To prevent unauthorized software installation without disrupting approved work, build in stages and verify how each control behaves on the Windows versions and device groups you actually manage.
- Inventory devices: Record Windows editions and versions, management methods, user groups, and approved applications.
- Reduce privileges: Give users standard accounts for routine work and reserve administrative access for authorized tasks.
- Select controls: Match account restrictions, application-control policies, and approved software deployment to your requirements.
- Pilot the configuration: Test with representative users and devices before expanding enforcement.
- Monitor and refine: Review blocked requests, installation activity, and support issues, then adjust rules as work needs change.
Restrict installation rights and manage administrator access
Role-based access keeps elevated permissions with the people and tasks that need them. Where organizational policy supports it, separate administrative credentials from everyday user accounts. IT can then deploy approved applications and updates through established administrative workflows instead of granting every user installation rights. Standard accounts can limit system-wide changes, but don’t assume they block every per-user installation. Confirm behavior with your Windows configuration and deployment methods.
Use application control to allow approved software
Application allowlisting permits software that matches defined organizational rules, such as publisher, file, or path criteria. AppLocker offers policy-based application control for suitable managed environments. Windows Defender Application Control provides a more robust option for organizations seeking stronger enforcement, though planning and policy design can be more demanding. Choose based on device requirements, operational capacity, and the level of control needed.
Group Policy can help configure and distribute policies in supported environments, while other management tooling may be used to deploy and maintain settings. Because controls can interact, verify the Windows edition and version, management tooling, policy precedence, and current Microsoft product names and support guidance before deployment. MITRE’s overview of mitigation M1033 also describes approaches such as limiting permissions and application control.
Start application-control rules in audit mode or with a limited pilot where available. Check whether business-critical apps, installers, and update mechanisms are affected before enforcing rules broadly. A blocked legitimate update can interrupt work, while a rule that’s too permissive may not provide the intended restriction. For shared endpoints, consider how preventive policies can be complemented by Windows system recovery tools if an unwanted change still affects a device.
Compare installation controls, monitoring, and rollback by what they actually do
These controls address different points in the software lifecycle. Account restrictions and application control can limit installation. Deployment provides a managed route for approved software. Monitoring helps administrators see activity, while rollback supports recovery afterward. To prevent unauthorized software installation effectively, choose each tool for its actual role rather than treating visibility or recovery as a preventive block.
| Approach | Purpose | Administrative effort and workflow impact | If a control fails |
|---|---|---|---|
| Account restrictions | Limit permissions, especially system-wide changes. | Moderate setup; users may need an approved process to request software. | Review the permissions and installation path; standard accounts may not block every per-user install. |
| Application control | Allow applications that meet defined rules and restrict others. | Higher planning and maintenance; rules can affect legitimate apps or updates if too broad. | Review policy results, logs, and exceptions, then adjust and test rules. |
| Software deployment | Deliver approved applications and updates through IT workflows. | Requires application packaging or deployment processes; can simplify routine installs for users. | Check deployment status and provide an approved alternative route for urgent software needs. |
| Monitoring | Surface application or installation activity for review. | Requires log review and clear alert ownership; usually has little direct workflow impact. | Investigate and respond. Visibility and alerts identify activity but don’t necessarily block installation. |
| Rollback | Restore system state after unwanted changes. | Requires recovery planning and validation; may affect changes made since the recovery point or baseline. | Use the appropriate recovery process, then confirm the system is ready for work. |
When permissions and application control are the right fit
Account restrictions are a practical fit where users don’t need local administrative rights for daily tasks. Application control is useful on endpoints that need a defined set of approved applications, such as shared computers with a consistent purpose. Neither removes the need for exceptions. Assign an owner and approval path for new applications, business-critical updates, and changes to allow rules. This keeps restrictions aligned with real work instead of forcing users to find workarounds.
When recovery controls add resilience
Recovery addresses a different problem. RollBack Rx Professional and RollBack Rx Server Edition use sector-level snapshots to support system rollback after an unwanted change. Reboot Restore Standard and Enterprise return protected systems to a configured baseline on restart, which can help maintain consistency on shared Windows computers. These capabilities support recovery, not real-time installation blocking or application allowlisting. Use them alongside preventive policy controls, and validate the recovery plan against your devices and operational needs.
How to implement software installation restrictions without disrupting work
Effective restrictions are built around how people and devices are used, not applied as a blanket rule. A staged rollout helps prevent unauthorized software installation while giving IT a chance to catch policy conflicts before they interrupt business-critical work.
- Inventory the environment: Identify device types, Windows configurations, user groups, approved applications, installers, and how each application receives updates.
- Define the policy: Set approval criteria, permitted installation routes, and which roles need exceptions. Document each exception’s owner, reason, approval period, and renewal or removal process.
- Test the configuration: Validate policies and recovery steps in a test environment that reflects production devices and management tools.
- Pilot, then enforce: Start with a representative group, review results, address conflicts, and expand enforcement in stages.
- Review regularly: Reassess rules after application or operating-system changes and when users’ roles change.
Provide a route for urgent, legitimate installations, such as a request reviewed by an authorized administrator and delivered through the approved deployment workflow. Make that process clear to users before restrictions go live.
Pilot policies and protect legitimate software updates
Begin in audit mode where available, or test with a limited group before enforcement. Include routine application updates, assistive tools, business-critical software, and IT deployment workflows in test cases. For each case, record the expected result and who can resolve a block. If a policy error prevents essential work, administrators should know how to adjust or withdraw the rule and restore the intended configuration.
Test recovery steps as well. Confirm who can authorize a policy change, how it will be reversed, and how affected devices will be checked before returning to service. Keep the test environment aligned with production policy and management settings. A materially different test environment may miss conflicts.
Monitor, review, and refine restrictions
After rollout, review available management reports and event logs for blocked or permitted activity. Assign an owner to investigate recurring blocks and track exception requests. Repeated requests for the same application or update may signal a gap in the approved software process, while unexpected activity may need further review. Monitoring provides visibility, but it should not be mistaken for a control that blocks installation.
Revisit rules after software changes, operating-system updates, and user-role changes. If an enforcement mistake affects system state, use the organization’s recovery procedure and validate the device before normal use resumes. Recovery products such as Reboot Restore or RollBack Rx can complement preventive policies. Confirm that their capabilities and deployment requirements fit your environment. Explore Windows endpoint recovery options as part of that planning.
Recover safely when an unauthorized installation gets through
Even a well-designed installation restriction plan needs a response for changes that slip through. Avoid rushing straight to removal or rollback. First determine whether the issue is an unwanted application, a broader configuration change, or a possible security incident. If compromise or sensitive data exposure is suspected, follow your organization’s incident procedures and involve the appropriate security personnel before making changes that could affect the investigation.
Use a measured response:
- Assess: Record what was installed, when it appeared, which account and device were involved, and whether other systems may be affected.
- Contain: Follow internal procedures to limit further impact while preserving information needed for investigation.
- Remove or restore: Use approved IT and endpoint security procedures to remove an unwanted application or recover from a broader system change.
- Validate: Confirm the device’s configuration and required applications are functioning, and verify that authorized changes and required user data have been preserved.
- Improve: Document the cause, review the relevant policy, and adjust controls or approval workflows to address the gap.
Choose between removing an application and restoring a system state
For a known, isolated application that hasn’t changed other system settings, approved removal may be the proportionate response. If the installation altered configuration more broadly, assess whether restoring a known-good state is appropriate. Suspected compromise calls for investigation under organizational procedures before choosing either action. A rollback can help return a system to an earlier state, but it doesn’t establish whether an account or another endpoint was affected. Check what changes may be lost and confirm that necessary data and authorized work are protected before proceeding.
Where Horizon DataSys recovery software fits
Recovery tools complement preventive controls; they don’t serve as application allowlisting or guaranteed real-time installation blocking. Reboot Restore Enterprise returns protected systems to a configured baseline on restart and provides centralized management for network environments, which can support baseline consistency on shared Windows devices. RollBack Rx Professional uses sector-level snapshots to support system rollback after unwanted changes. Confirm product capabilities and deployment requirements for your environment, and make sure the recovery process fits investigation and data-preservation needs.
For more detail, read the reboot-to-restore software guide and the Reboot Restore Enterprise evaluation guide. A defined recovery path strengthens efforts to prevent unauthorized software installation while keeping response decisions grounded in the actual impact of each change.
Build a Windows environment that stays controlled and recoverable
A reliable plan to prevent unauthorized software installation combines proportionate user permissions, application controls, and an approved route for software deployment. Pilot rules before broad enforcement, then review activity and exceptions so legitimate applications and updates remain manageable.
Prevention and recovery have different jobs. Policies can restrict unapproved applications, while monitoring helps reveal activity and a recovery plan helps address changes that get through. Reboot Restore products return protected systems to a configured baseline upon restart, and Reboot Restore Enterprise adds centralized management for network environments. RollBack Rx products support snapshot-based system rollback. These capabilities can help restore system state, but they aren’t substitutes for application allowlisting or security investigation.
If recovery is part of your endpoint plan, explore Horizon DataSys endpoint recovery solutions to consider options that fit your environment. With tested controls, a clear approval path, and a defined recovery process, your team can strengthen system consistency while keeping essential work moving.
Frequently Asked Questions
How can I prevent users from installing unauthorized software on Windows?
To prevent unauthorized software installation, combine standard user accounts with application-control policies and an approved process for deploying applications and updates. First inventory your Windows versions, devices, software, and user roles. Then pilot the chosen controls with representative users, check for blocked business applications, and adjust before wider enforcement. Monitoring can surface activity for review, while a documented recovery process helps administrators respond if an unwanted change still affects a device.
Can standard users install software on Windows?
Yes, some standard users can install certain applications, depending on the installer, where it writes files, and the device’s Windows configuration. Software that needs system-wide changes or elevated permissions may require administrator approval, but a standard account isn’t a guarantee that every installation is blocked. Test common installers and per-user application behaviors in your environment. Add application-control policies if your requirements call for more precise restrictions.
Does Group Policy block all software installation?
No. Group Policy can configure and distribute supported settings, but it doesn’t automatically block every installer or application. The result depends on the specific policy, Windows edition and version, management setup, and how the software installs. Test policy interactions on representative devices, including approved deployment and update workflows. Use application control where you need rules defining which software may run, and verify current Microsoft documentation for applicable support.
What is the difference between AppLocker and Windows Defender Application Control?
AppLocker provides rules that can control which applications users or groups are allowed to run. Windows Defender Application Control, also referred to in newer Microsoft materials by updated naming, is a more robust application-control approach designed for stronger enforcement. It can require more planning and policy management. Check Microsoft’s current terminology, feature support for your Windows editions, and your management tools before choosing or deploying either option.
Can application allowlisting block software updates?
Yes. If an update’s installer or updated application doesn’t meet the allowlisting rules, the policy may block it and interrupt normal work. Before enforcement, identify update mechanisms, publishers, installers, and applications that must remain available. Test routine updates through your approved deployment workflow, review audit or pilot results, and document an exception process with an owner. Reassess rules when applications or update methods change.
Does reboot-to-restore software prevent unauthorized software installation?
No. Reboot-to-restore is a recovery and configuration-consistency approach, not a real-time installation block or application allowlisting policy. Reboot Restore products return protected systems to a configured baseline upon restart, which can help maintain shared Windows computers. Administrators still need preventive controls to restrict unapproved software. Confirm product capabilities and deployment requirements for the environment, and plan how to preserve authorized changes and required user data.
What should IT do after an unauthorized application is installed?
Assess what was installed, when, and whether the change affected only one application or broader system settings. Follow organizational incident procedures if compromise or sensitive data exposure is suspected. Otherwise, use approved endpoint and IT processes to contain the issue, remove the application or restore a suitable system state, and validate the device and required data afterward. Review the cause and refine policies or approval workflows to reduce repeat occurrences.