What if the right alternative to reimaging isn’t another way to rebuild a computer, but a recovery method matched to the problem? For IT teams weighing alternatives to reimaging computers, that distinction matters: repeated rebuilds take staff time and interrupt user access, even when an endpoint only needs to return to a known-good state.
Reimaging still has a place, particularly when deploying devices or rebuilding systems that need a fresh start. But shared computers, remote devices, and systems that need recovery to an earlier point may call for different approaches. The key is to maintain consistent configurations without making a full rebuild the default response to every issue.
This guide compares five practical approaches, explains how each provisions or restores endpoints, and shows where it fits best. You’ll look at deployment automation, reboot-to-restore, snapshot rollback, configuration management, and nonpersistent desktops. By weighing device ownership, persistence, and recovery needs, you can choose a model that reduces hands-on rebuilding while keeping endpoints predictable.
Key Takeaways
- Match the recovery method to the event you need to address, from new-device setup to restoring a previous system state.
- Compare five alternatives to reimaging computers by how they work, where they fit, and whether they replace or streamline imaging.
- Consider whether endpoints are shared or individually assigned, and whether they need to preserve changes between sessions.
- Use reboot-to-restore to return shared Windows computers to a clean baseline after restart, or snapshot rollback when returning to an earlier system state is the priority.
- Choose a recovery model that balances endpoint consistency, user access, and the level of control your IT team needs.
Why IT teams look for alternatives to reimaging computers
Computer reimaging rebuilds a device’s operating system and configuration from a prepared image. It can restore a known setup, but repeated imaging for routine issues may involve scheduling work, coordinating device access, reinstalling or updating components, and checking the endpoint before returning it to the user. That effort can be difficult to justify when the issue is a temporary change or a recoverable system fault.
The key distinction is between preparing a device and recovering one. A new computer or a device being refreshed may need a full, standardized setup. A computer that has already been provisioned may instead need its shared-use baseline restored or its system state returned to an earlier point. Those goals call for different recovery behavior. The right choice also depends on whether user data and approved changes should persist.
Provisioning sets up a device; reset returns it to a defined baseline; rollback restores an earlier system state. These approaches can reduce routine imaging without eliminating imaging’s role in deployment or major rebuilds. They also differ in what they preserve, so plan recovery around the endpoint’s purpose and the data users need to keep.
When traditional imaging is still the right tool
Imaging remains useful for initial device provisioning and hardware refreshes, when IT needs to apply a known operating-system and application configuration across a group of computers. It creates a repeatable starting point, especially when devices must be prepared before use. The question isn’t whether imaging is obsolete; it’s whether a full image deployment is the most suitable response to recurring changes or problems after setup.
What “alternative” means in endpoint recovery
An alternative may rebuild less, or not rebuild at all. A reset can return a shared computer to a controlled baseline, while rollback can revert system changes to a captured earlier state. A basic recovery feature such as System Restore illustrates the idea of reversing system changes without a full reimage. For shared endpoints, reboot-to-restore software fundamentals explain another baseline-focused model. Choose based on what needs recovery, which user changes should persist, and whether the device is shared or individually assigned.
Five alternatives to reimaging: deployment to rollback
The right choice depends on what needs to be restored. Some approaches make initial setup more repeatable; others return a computer to a baseline or earlier state after a problem. These alternatives to reimaging computers address different operational needs, and several can complement rather than replace imaging.
Deployment automation and configuration management
Automated deployment tools standardize device provisioning and reduce manual setup steps, but may still rely on images. SmartDeploy, for example, is a third-party option that streamlines image deployment across hardware. Configuration management tools and scripts apply or maintain settings on managed endpoints. They can help enforce a desired configuration, but aren’t automatically full recovery systems if an operating system becomes unusable.
Windows also includes recovery options for repair tasks. Microsoft’s documentation on the Windows Recovery Environment describes tools that support recovery and troubleshooting. These options address repair, while deployment automation focuses on preparing devices.
Reboot resets, snapshots, and nonpersistent desktops
Reboot-to-restore returns a shared endpoint to a defined baseline after restart, making it suited to environments where changes from one session shouldn’t carry into the next. Snapshot rollback instead reverts a system to a captured point, which can help when a particular earlier configuration is the desired recovery target. Nonpersistent desktops discard session changes in a virtualized desktop model. Unlike endpoint recovery software, virtual desktop infrastructure requires a separate architecture and operational resources to deliver and manage virtual desktops.
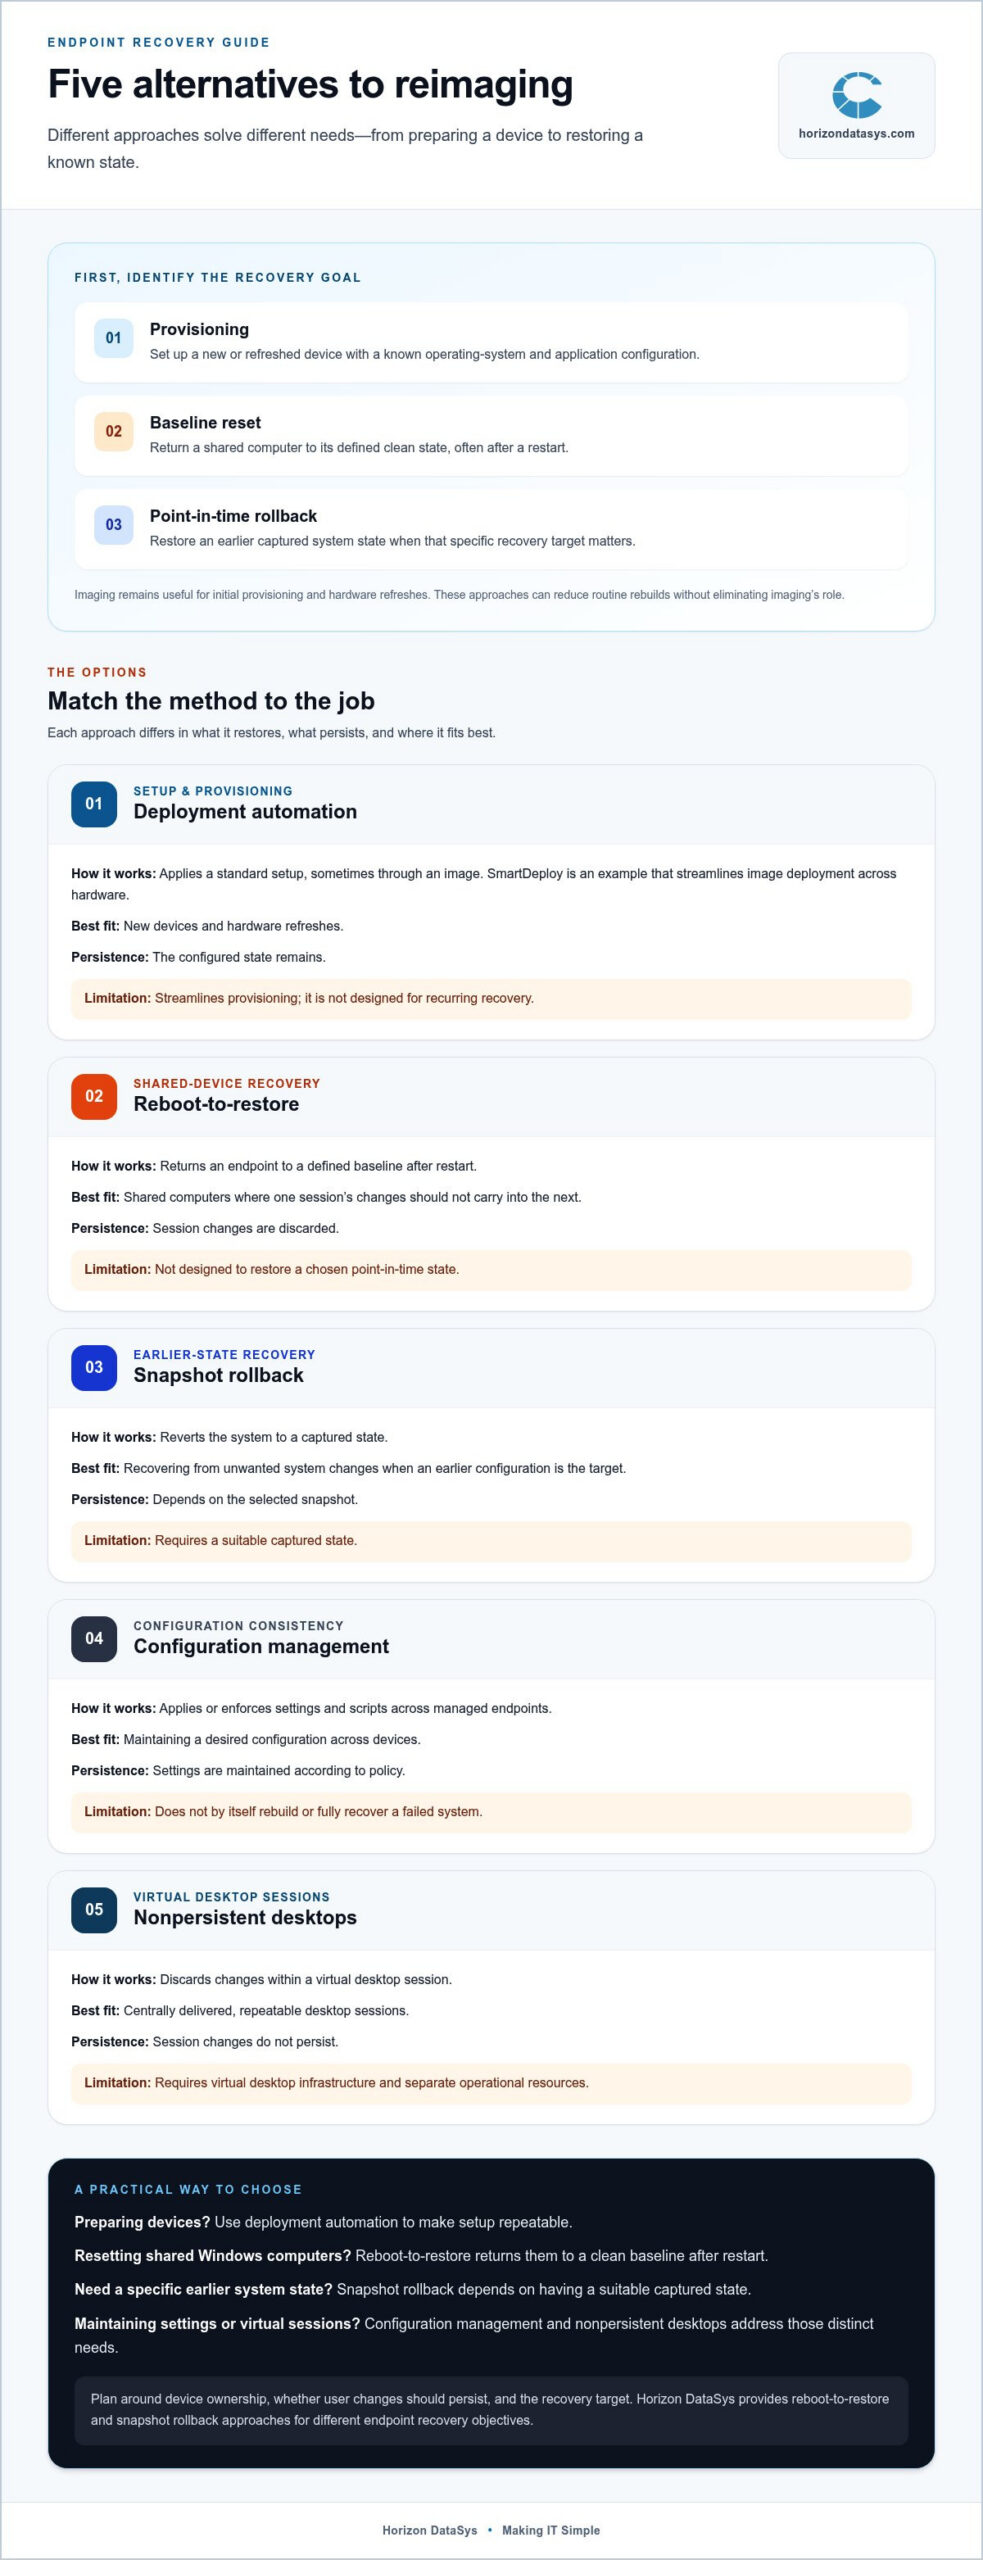
Automated deployment
Mechanism: Applies a standard setup, sometimes through an image. Best fit: New devices and refreshes. Persistence: Configured state remains. Limitation: Streamlines provisioning, not recurring recovery.
Reboot-to-restore
Mechanism: Returns the endpoint to a baseline after restart. Best fit: Shared computers. Persistence: Session changes are discarded. Limitation: Not designed to recover a chosen point-in-time state.
Snapshot rollback
Mechanism: Reverts the system to a captured state. Best fit: Recovering from unwanted system changes. Persistence: Depends on the selected snapshot. Limitation: Requires a suitable captured state.
Configuration management
Mechanism: Applies or enforces settings and scripts. Best fit: Maintaining configuration across managed devices. Persistence: Settings are maintained according to policy. Limitation: Doesn’t by itself rebuild or fully recover a failed system.
Nonpersistent desktops
Mechanism: Discards changes within a virtual desktop session. Best fit: Centrally delivered, repeatable desktop sessions. Persistence: Session changes don’t persist. Limitation: Requires virtual desktop infrastructure.
For shared Windows computers, Horizon DataSys’ endpoint recovery software provides reboot-to-restore and snapshot rollback approaches. Each is designed for a different recovery objective.
Compare reimaging alternatives by recovery speed, persistence, and control
These approaches differ in what they restore and which changes they retain. Deployment recreates a device setup; reboot-to-restore returns an endpoint to a defined baseline; snapshot rollback restores a captured system state; configuration management reapplies settings; and a nonpersistent desktop discards changes from a virtual session.
Deployment prepares a device for use, while rollback recovers a system from a selected earlier state. Treating them as interchangeable can leave a gap. A deployment process may standardize setup without addressing frequent recovery, while a rollback method may restore a system without managing the configuration of an entire fleet.
Which approaches preserve or discard user changes?
Persistence is a deliberate design choice. Reboot resets discard session changes as they return shared computers to a clean baseline. Snapshot rollback returns the system to a selected earlier point, so changes made after that point may no longer be present. Nonpersistent desktops discard session changes by design. Before selecting among alternatives to reimaging computers, distinguish system recovery from user-data protection. Don’t assume recovery tools or workflows replace separate backup arrangements for files users need to keep.
Which model fits shared computers or managed fleets?
Shared computers in public, educational, or similar environments often benefit from predictable reset behavior after sessions. Standardized fleets may need deployment and configuration controls to establish or maintain settings across devices. Snapshot recovery fits cases where administrators need to return a system to a captured state. Broader endpoint management provides a policy-based framework for overseeing devices, but it serves a different purpose from restoring a particular endpoint after a failure.
- Automated deployment: Restores device setup. It can establish a standard starting point, but typically streamlines provisioning rather than recurring recovery. Persistence begins with the deployed configuration.
- Reboot-to-restore: Restores a defined baseline after restart. It suits shared endpoints where user changes shouldn’t persist between sessions. Reboot Restore Enterprise adds centralized management for network environments.
- Snapshot rollback: Restores a captured system state. RollBack Rx uses sector-level snapshots and operates below Windows, supporting system rollback without full drive reimaging. Recovery timing depends on the system and selected recovery process.
- Configuration management: Maintains or reapplies settings across managed devices. Its control can support fleet consistency, but scripts and policies alone aren’t a complete system-recovery method.
- Nonpersistent desktops: Restore a clean virtual session by discarding session changes. They suit virtual desktop environments, but require a separate virtualized architecture and operational model.
How to choose a computer reimaging alternative for your environment
Selecting among alternatives to reimaging computers starts with the recovery event, not the tool. A method suited to clearing session changes on shared PCs may not be right for a failed update on an individually assigned workstation. Use this process to match recovery behavior to endpoint needs and administrative workflows.
Start with the failure or change you need to reverse
- 1. Define the recovery event. Is the goal routine session cleanup, recovery from system corruption or a failed update, or reversal of an unwanted configuration change? Scheduled hardware refreshes may still call for image-based provisioning rather than ongoing recovery.
- 2. Decide what should happen to changes. Identify which user files and approved system changes must remain available. A reboot reset returns an endpoint to its baseline, while snapshot rollback returns it to a selected earlier system state. Neither should be treated as a substitute for separate user-data protection.
- 3. Set the recovery trigger. Should the endpoint reset automatically on restart, or should an administrator select a captured state when needed? That distinction helps separate shared-device cleanup from targeted system recovery.
Validate deployment, management, and operational fit
- 4. Map the endpoint environment. Note whether devices are shared or individually assigned, whether changes should persist between sessions, and whether endpoints are rebuilt during scheduled refreshes. Consider existing Windows management workflows, administrator access, and the number of devices that need consistent control.
- 5. Pilot representative devices. Test the method on devices that reflect real hardware and usage patterns. Exercise routine changes and recovery scenarios, such as a configuration issue or failed update, then check the resulting system state and user access.
- 6. Document the operating rules. Record the approved baseline, when to reset or roll back, which data must be retained, and how exceptions or approved updates are handled. Clear procedures help administrators apply recovery consistently across a fleet.
For shared-PC environments that need centralized administration, assess how Reboot Restore Enterprise fits your management workflow. A pilot and written recovery procedure can help establish whether the approach fits the team’s day-to-day operations.
Explore endpoint recovery approaches to compare baseline restoration and system rollback for Windows environments.
How Horizon DataSys supports recovery without full computer reimaging
Two recurring recovery needs call for different approaches: returning a shared computer to a consistent baseline after use, or restoring a system to a selected earlier state after an unwanted change. Horizon DataSys provides Windows endpoint resilience software for both patterns. These alternatives to reimaging computers can reduce routine full-drive rebuilds, but they aren’t a substitute for every provisioning process or for separate user-data backup requirements.
Reboot Restore for consistent shared-computer sessions
Reboot Restore Standard and Reboot Restore Enterprise automatically return shared computers to a clean baseline upon restart. This model suits environments such as public access or educational settings, where users make temporary changes during a session and the next person should start from a known configuration. It addresses recurring session cleanup after a computer has been set up, rather than initial deployment of a new device.
For network environments, Reboot Restore Enterprise includes centralized management. Administrators can manage the reboot-to-restore approach across shared endpoints while maintaining a consistent baseline. The key operational distinction is the trigger: restoration is tied to restart, rather than an administrator selecting a particular earlier system state.
RollBack Rx for rapid system-state recovery
RollBack Rx Professional and RollBack Rx Server Edition use sector-level snapshots to support rapid rollback without full drive re-imaging. The software operates below the Windows operating system layer, and rollback returns the system to a captured state. Snapshot recovery fits when the priority is reversing unwanted system changes, rather than automatically clearing session changes at each restart.
The edition names reflect different endpoint scopes: RollBack Rx Professional is for professional desktop environments, while RollBack Rx Server Edition is intended for server environments. Both use snapshot-based rollback. Choose according to the type of system you need to recover and the technical requirements of your environment.
Neither approach is a universal replacement for imaging. New-device provisioning may still require a deployment process, and files users need to retain call for separate data-protection planning. Match the recovery method to the event: automatic baseline restoration for shared sessions, or administrator-directed rollback to a captured state.
Explore Horizon DataSys recovery software to find the recovery approach that fits your endpoint environment.
Build a recovery model around your endpoints
The best alternatives to reimaging computers depend on the task: provisioning a device, clearing changes between shared sessions, or returning a system to an earlier state. Deployment, reset, and rollback serve different purposes, so match the method to endpoint ownership, persistence needs, and the recovery event your team handles most often.
For shared Windows computers, Reboot Restore returns devices to a clean baseline on restart, while Reboot Restore Enterprise adds centralized management tools for network environments. When recovery to a captured system state is the priority, RollBack Rx uses sector-level snapshots for rollback without full drive re-imaging. These approaches can reduce routine rebuilds, while data protection and new-device provisioning may still require separate processes.
Start with a representative pilot, define which changes and files must persist, and document how administrators will reset or roll back endpoints. A clear recovery model helps your team maintain consistency without treating every issue as a reason to rebuild. Explore Horizon DataSys recovery solutions and identify an approach that fits your environment.
Frequently Asked Questions
What are the best alternatives to reimaging computers?
The best option depends on whether you need to set up devices or recover them after changes. Automated deployment streamlines provisioning, while configuration management applies or maintains settings across managed endpoints. Reboot-to-restore returns shared computers to a baseline after restart, and snapshot rollback restores a captured system state. Nonpersistent desktops discard session changes in a virtualized environment. Compare what each method restores, which changes persist, and how it fits your device fleet.
Can endpoint management software replace computer reimaging?
Endpoint management can reduce routine reimaging, but it doesn’t necessarily replace imaging or provide full recovery. Management tools can deploy settings, applications, and policies across enrolled devices, helping maintain consistency. If an operating system needs a clean rebuild, imaging may still be appropriate; if a system needs to return to a prior state, rollback may be a better fit. Treat configuration control and system recovery as related but distinct capabilities.
Is reboot-to-restore software the same as computer reimaging?
No. Reimaging rebuilds a computer’s operating system and configuration from an image, while reboot-to-restore returns a protected computer to a defined baseline after restart. Reboot Restore is designed for shared Windows computers that should begin sessions in a consistent state. It supports recurring cleanup after use, rather than serving as a new-device provisioning method. The distinction is the recovery action: rebuilding from an image versus resetting to an established baseline.
How does snapshot rollback differ from restoring a backup?
Snapshot rollback returns a system to a captured earlier state, which can reverse system changes without repeating a full drive reimage. RollBack Rx uses sector-level snapshots and operates below Windows. A backup has a different purpose: keeping a recoverable copy of files or systems for data protection. Don’t assume rollback replaces backup, or that either approach alone covers every recovery need. Define which system state and user data must be recoverable.
What happens to user files when a computer resets on reboot?
A reboot-to-restore system returns the protected computer to its defined baseline, so changes made during a session may be removed. Don’t assume user-created files will persist unless their storage and protection are specifically accounted for in your setup. Before deployment, identify where users should save files, determine which approved changes must remain, and test the reset behavior on representative devices. Maintain separate data-protection processes for files that need to be retained.
When should an IT team still use computer imaging?
Imaging remains useful for initial device provisioning, hardware refreshes, and rebuilds that require a known operating-system and application configuration. It can provide a standardized starting point for new or replacement computers. For recurring session cleanup or recovery from a captured system state, a reset or rollback approach may avoid rebuilding the entire device. Choose based on the event: deployment, scheduled refresh, or recovery after an issue.