What if the simplest way to keep a Windows PC clean is to control what can run, rather than relying on users to avoid risky downloads? If you’re deciding how to stop users from installing software, the challenge is balancing consistent restrictions with legitimate work needs. Broad administrator access can make it easier to add unapproved applications, while repeated manual cleanup can keep IT teams busy.
Windows offers several ways to limit software installation. The right approach depends on the control your environment needs and the administrative effort it can support. A restriction that is too loose may leave gaps; one that is too strict can disrupt approved tasks. The goal is to apply policy consistently while giving users the applications they need without granting unnecessary privileges.
This guide explains how to choose and apply Windows controls, including application-control policies, and how to plan for exceptions. It also covers recovery when unwanted changes still occur. Reboot Restore complements installation restrictions by restoring protected computers to a clean baseline on restart. It helps keep shared PCs consistent, but it is not a real-time installation blocker.
Key Takeaways
- Learn how to stop users from installing software by combining standard-user permissions with application controls suited to your Windows environment.
- Compare control methods by where they enforce restrictions, how they handle exceptions, and the administrative effort they require.
- Inventory approved applications, user roles, and installation workflows before piloting restrictions with representative users.
- Use least privilege, application controls, and monitoring together to reduce unauthorized changes without blocking legitimate work.
- For shared PCs, consider reboot-to-restore as a recovery layer that returns protected computers to a clean baseline when they restart.
How to stop users from installing software: understand the control layers
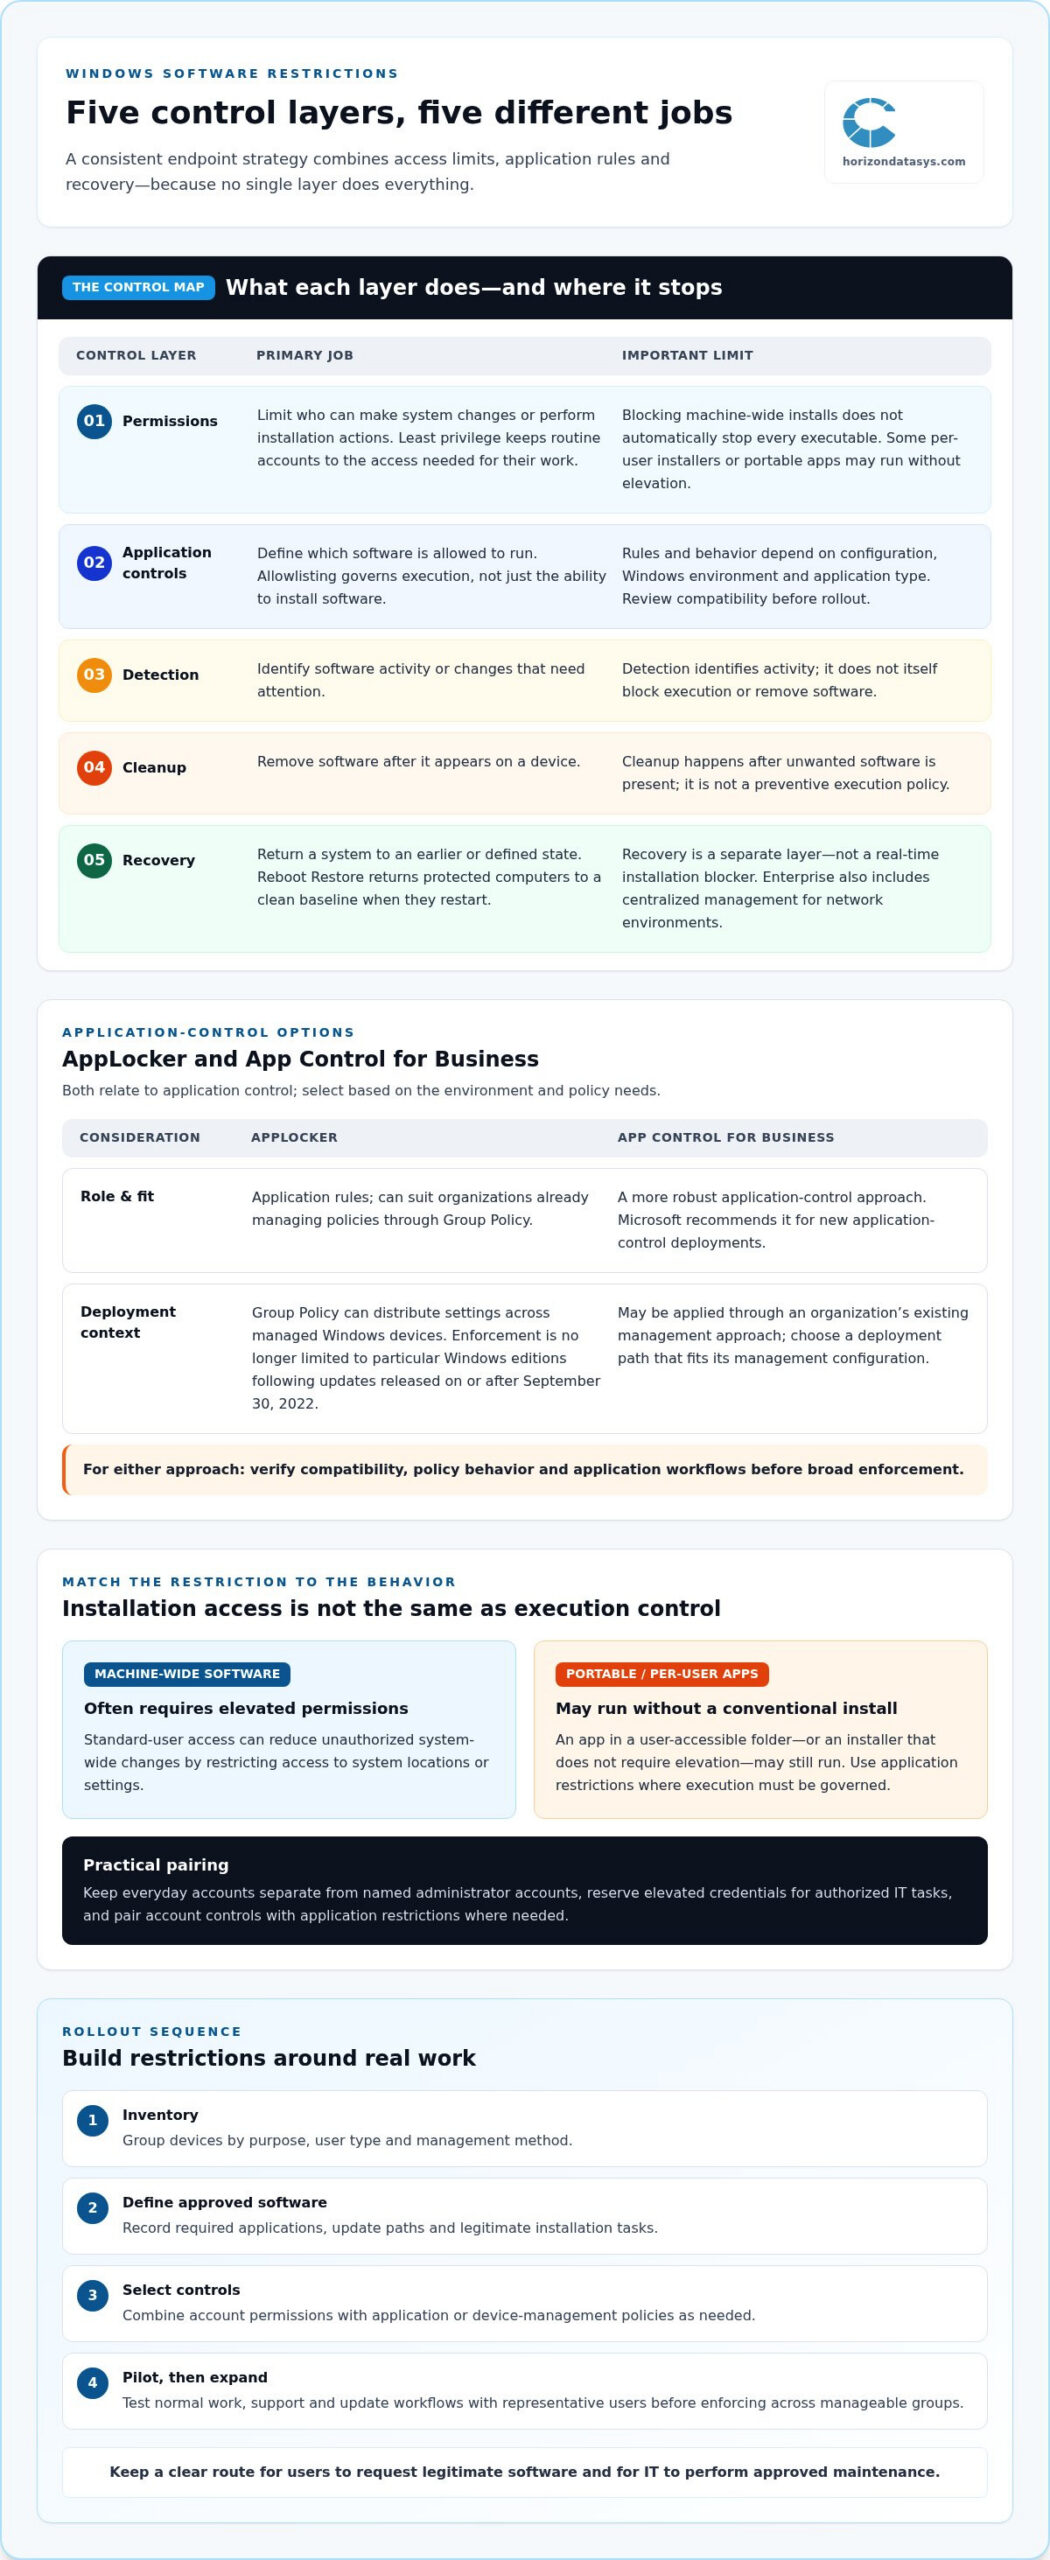
To decide how to stop users from installing software, first identify which actions you need to control. Installation restrictions limit who can add software. Application controls determine what can run. Detection identifies activity, while cleanup removes software after it appears. Recovery is different: it returns a system to an earlier or defined state. These layers can work together, but they do not perform the same job.
This distinction matters on shared PCs in libraries, computer labs, and workplaces. A user might install an application for all accounts, run a portable app from a folder, or change settings that affect only their profile. A permission that blocks one installation route may leave another open. Application controls can govern which software is allowed to run. AppLocker is one example of application whitelisting technology. Its exact behavior depends on the Windows edition, configuration, and application type.
Consistent endpoint management therefore takes more than one setting. Access management limits users’ ability to make system changes, application controls define what may run, and recovery addresses unwanted changes that get through. No single layer provides every kind of enforcement or restores a clean baseline by itself.
What does preventing software installation actually control?
Permissions can restrict installation actions, particularly changes that require access to system locations or settings. They do not automatically block every executable. Machine-wide software is installed for use across accounts and commonly needs elevated permissions. Portable applications may run from a user-accessible folder without a conventional installation process. Blocking system-wide installation alone may not prevent them from launching, so match the control to the behavior you need to govern.
Why standard-user access is the starting point
Least privilege means routine accounts have only the permissions needed for their work. Keep administrator credentials separate and reserve them for authorized IT tasks. This reduces opportunities for users to make unauthorized system-wide changes, but it is not a complete application policy: standard accounts may still run per-user applications or installers that do not require elevation. Pair account controls with application restrictions where needed.
For shared endpoints, treat recovery as a separate layer, not an installation blocker. Reboot Restore Standard and Reboot Restore Enterprise return protected computers to a clean baseline when they restart. Enterprise also includes centralized management for network environments. This helps maintain a consistent state between sessions, while installation and execution restrictions govern what users can do during those sessions.
How to prevent software installation with Windows permissions and application controls
Effective restrictions start with a deployment plan, not a blanket block. To determine how to stop users from installing software across an environment, map devices and their roles, identify approved applications, and select controls that match the required level of enforcement. Pilot the controls with representative users before applying them broadly. A staged rollout can reveal workflow conflicts while policies are still easy to adjust.
- Inventory: Group devices by purpose, user type, and management method.
- Define approved software: Record required applications, update paths, and legitimate installation tasks.
- Select controls: Combine account permissions with application or device-management policies as needed.
- Pilot and enforce: Test normal work, support, and update workflows, then expand in manageable groups.
Set up standard accounts and administrative permissions
Keep everyday accounts separate from named administrator accounts, and reserve elevated credentials for authorized IT personnel. Document how approved installations and maintenance are requested and performed. Users need a clear route to obtain legitimate software. Test that process alongside routine updates and support tasks before enforcement, so reducing unnecessary elevation does not create a dead end.
Choose application control for approved-software enforcement
Allowlisting defines which applications may run, rather than relying only on users lacking installation permissions. Group Policy can distribute settings across managed Windows devices, while mobile device management can apply policy through an organization’s existing management platform. Choose the deployment path that fits the environment and its management configuration.
AppLocker offers application rules and can suit organizations already managing policies through Group Policy. Windows Defender Application Control, now referred to as App Control for Business in Microsoft documentation, provides a more robust application-control approach; Microsoft recommends it for new application-control deployments. Microsoft’s overview can help administrators choose when to use App Control or AppLocker. AppLocker policy enforcement through Group Policy is no longer limited to particular Windows editions following updates released on or after September 30, 2022. Compatibility and policy behavior still need review.
Before rollout, verify the Windows editions, update levels, licensing, management tools, and application types in scope. Build and test rules against approved software, including its update and support processes. An incomplete allowlist can block legitimate work. Record exceptions and assign responsibility for maintaining them instead of weakening policy across every device.
Application controls govern what can run, while recovery addresses changes that still occur. For shared endpoints, Windows endpoint recovery options complement enforcement by helping restore a clean baseline after restart. They do not block installation during an active session.
Which installation-blocking method fits your Windows environment?
The right method depends on what you need to prevent and how consistently you need to apply the restriction. Standard accounts reduce users’ ability to make system-level changes; application controls decide which software can run; centralized policy helps administer rules across devices. Recovery tools serve a different purpose by addressing changes after they happen. To choose how to stop users from installing software, compare each layer by its enforcement point and operational role.
| Method | Enforcement point | Administration and exceptions | Recovery role |
|---|---|---|---|
| Standard-user permissions | Limits actions that require elevated system access. | Usually a straightforward baseline; approved installs and maintenance need a controlled elevation process. | Does not restore changes. |
| Application allowlisting | Restricts which applications or executable types can run, according to configured rules. | Requires rules for approved software and a process for exceptions, updates, and new apps. | Does not undo changes already made. |
| Centralized policy | Delivers and manages settings across a group of devices. Group Policy or device-management tools can distribute policies; the configured policy provides the actual control. | Reduces device-by-device administration, but groups, assignments, and exceptions still need maintenance. | Does not itself recover a device. |
| Reboot restoration | Returns a protected computer to a clean baseline when it restarts. | Useful for shared endpoints; plan which baseline should be restored and how legitimate changes are maintained. | Restores the baseline after restart; it is not an installation blocker. |
When account restrictions are enough, and when they are not
Standard accounts are a sensible foundation for routine workstations and shared devices where users do not need administrator privileges. They can limit system-wide installations, but they may not stop portable applications or per-user installs that work within a user’s profile. If users should run only a defined set of applications, add application control and test its rules against approved software.
How restoration differs from blocking an installation
Reboot Restore Standard and Reboot Restore Enterprise return protected computers to a clean baseline on restart. Enterprise also includes centralized management for network environments. This helps shared PCs begin sessions from a consistent state, but it does not prevent software from being installed during an active session. RollBack Rx Professional and RollBack Rx Server Edition use sector-level snapshots for system rollback when recovery is needed. Neither approach replaces access policies or application controls.
Choose account restrictions for a permissions baseline, add allowlisting when you need defined software rules, and use centralized policy to manage enforcement across devices. Treat recovery as a complementary layer, not a substitute for blocking installation or execution.
How to roll out software-installation restrictions without disrupting users
A restriction that works on a test machine can still disrupt a team if it blocks an approved update, assistive tool, or line-of-business application. Before broad enforcement, map the environment and document how software is legitimately installed. This gives administrators a basis for deciding which rules to apply, where exceptions may be needed, and how to respond when a policy blocks expected work.
Start by documenting:
- Installed applications: Include versions, update methods, and software dependencies.
- Devices and user roles: Identify shared endpoints, specialist workstations, and groups with different application needs.
- Installation workflows: Record who approves, installs, and maintains software, including support and update tasks.
Use the inventory to define approved applications and group devices with similar requirements. Pilot the selected restrictions with representative users before expanding enforcement. A lab or shared-device group may reveal different issues than an office workstation, so include realistic tasks from each intended deployment group.
Test policies before enforcing them broadly
Where the chosen control supports audit or evaluation mode, use it to identify software that would be blocked before enabling enforcement. Test installers, routine updates, assistive tools, support utilities, and business applications. Review policy events alongside user feedback. A successful test confirms both that unapproved software is restricted and that essential workflows remain available. Verify policy rollback and recovery access before production deployment.
Expand in controlled stages, keeping a record of policy versions, affected device groups, test results, and rollback steps. If a restriction causes disruption, pause expansion and investigate the specific rule or application. Make a documented change instead of applying a broad exception. This keeps policy updates traceable and avoids weakening protection across the environment to resolve one issue.
Manage exceptions and keep controls current
Assign approval authority to a defined role. Record each exception’s purpose, affected devices or users, approver, and review or expiry date. Monitor blocked attempts and support requests after rollout to identify policy gaps and legitimate software needs. Review application rules as approved software, business workflows, and device groups change, and remove exceptions that are no longer needed.
For a blocked configuration change that needs to be reversed, follow a documented recovery process and restore the intended settings. Keep this process distinct from application-policy exceptions, which determine what users may install or run. Add a recovery layer for protected Windows endpoints with endpoint recovery options that help return computers to a clean baseline on restart.
Maintain a clean baseline after restricting software installations
Installation restrictions reduce the changes users can make, but they cannot guarantee that every unwanted change is prevented. A resilient endpoint plan combines least-privilege accounts, application controls, monitoring, and a recovery method. Each layer has a distinct role: deciding who can make changes, what software can run, what activity needs attention, and how to restore system integrity if a change causes problems.
Recovery is especially useful for shared computers, where users need a consistent starting point from one session to the next. Reboot-to-restore returns a protected computer to its clean baseline when it restarts. It does not stop a user from installing or running software during an active session, so use it alongside the permissions and application policies selected to stop users from installing software.
Where Reboot Restore fits in a layered approach
Reboot Restore Standard and Reboot Restore Enterprise restore protected computers to a clean baseline on restart. This helps keep shared endpoints, such as lab or library PCs, consistent between sessions even when changes occur during use. Reboot Restore Enterprise includes centralized management for network environments, making it relevant when administrators need to manage protected computers across a network. For a deeper explanation of the mechanism, see the Reboot to Restore Software guide.
Think of restoration as the reset layer in an endpoint plan, not the gate at the point of installation. Application-control rules and account permissions govern user actions; reboot restoration helps return the device to its intended state afterward. Keeping those roles separate helps set clear expectations and prevents reliance on recovery as the only safeguard.
Choose recovery based on the endpoint problem
For shared PCs that should return to a known configuration between sessions, reboot restoration provides a repeatable baseline. When the need is to roll a system back after a problematic change, RollBack Rx Professional and RollBack Rx Server Edition use sector-level snapshots for system rollback without full-drive re-imaging. Choose the recovery approach based on whether the priority is a routine baseline reset or rollback to a system state.
Combine the selected recovery method with access controls, approved-software rules, and monitoring. Horizon DataSys solutions support Windows recovery and baseline management, while installation enforcement remains the role of Windows permissions and application controls.
Build a controlled, recoverable Windows environment
A dependable approach to how to stop users from installing software starts with least-privilege accounts, then adds application controls suited to each device group. Pilot policies before enforcing them broadly, and maintain a clear process for approved apps and exceptions. This helps protect system integrity without interrupting essential work.
Prevention and recovery serve different purposes. Windows permissions and application controls govern what users can install or run; recovery helps restore a system when unwanted changes still occur. Reboot Restore returns protected computers to a clean baseline on restart, while Reboot Restore Enterprise adds centralized management tools for network environments. For cases that call for rollback, RollBack Rx provides sector-level snapshots.
For shared PCs or managed endpoints, pairing consistent installation policies with a suitable recovery layer can support stable, maintainable systems. Explore Horizon DataSys endpoint recovery solutions to find an approach that complements your Windows controls. With a measured rollout and a reliable recovery path, your team can strengthen endpoint consistency while keeping legitimate work moving.
Frequently Asked Questions
How do I stop standard users from installing software on Windows?
Use standard accounts for routine work, reserve administrator credentials for authorized IT tasks, and add application controls if users must be limited to approved software. Standard-user permissions restrict many system-wide installation actions, but may not block portable applications or software installed within a user profile. Inventory required apps and test policies against normal workflows, updates, and support tasks before enforcing them across all devices.
Can Group Policy block users from installing software?
Yes. Group Policy can distribute settings that restrict software installation or application execution, depending on the policies configured and the Windows environment. Administrators can use it to manage application-control rules or related restrictions across domain-managed computers. The appropriate policy, supported Windows edition, update level, and deployment behavior can vary, so validate current Microsoft guidance and test the configuration before applying it broadly.
Is removing local administrator rights enough to prevent software installation?
No. Removing routine users’ local administrator rights is a valuable baseline because it limits system-wide changes that require elevation, but it does not block every installation route. Some applications can install within a user’s profile, and portable programs may run without a conventional installation. Pair least-privilege accounts with application controls when you need to define what users can run, and maintain an approval process for legitimate software requests.
How can I block users from installing unapproved applications?
Start by identifying approved software and the devices or user groups that need it. Combine standard-user permissions with an application-control policy that allows trusted applications and restricts others. Windows options include AppLocker and Windows Defender Application Control, also called App Control for Business. Configuration and support depend on the environment. Pilot rules first, including application updates and support tools, and create a controlled process for approving exceptions.
Does reboot-to-restore software stop users from installing software?
No. Reboot-to-restore software does not block installation during an active session. Reboot Restore Standard and Reboot Restore Enterprise return protected computers to a clean baseline when they restart, which can help keep shared PCs consistent between sessions. Use Windows permissions and application controls to restrict installation or execution, and treat reboot restoration as a complementary recovery layer for changes that still occur.
What is the difference between blocking installations and restoring a computer on reboot?
Blocking installations uses permissions or application-control rules to restrict who can install software or which applications can run. Restoring on reboot acts afterward: it returns a protected computer to its defined clean baseline when the system restarts. Reboot Restore supports this baseline-restoration approach. For targeted system rollback, RollBack Rx Professional and RollBack Rx Server Edition use sector-level snapshots. Recovery and prevention address different stages, so one should not replace the other.
How do I allow approved software while blocking other installations?
Build an inventory of required applications, including their update and support processes, then configure application-control rules to allow approved software and restrict unapproved applications. Keep routine user accounts separate from administrator accounts, and define who can approve exceptions and how decisions are recorded. Test the policy with representative users before full enforcement. Monitor blocked activity and support requests so legitimate workflows remain available without granting broad administrator access.