What if a computer could return to a known-good baseline every time it restarts, without staff having to undo each user’s changes? On shared Windows computers, settings, files, and installed software can drift from the intended setup, making manual cleanup a recurring and inconsistent task. The goal when you freeze computer state on restart is to keep each session from changing the environment the next user inherits.
Choosing the right protection takes more than asking whether changes disappear after a reboot. Consider how people use the computers, how many endpoints administrators manage, and whether you need automatic cleanup or a way to recover from a specific system problem. Restart-based protection can maintain a consistent baseline, but it isn’t a substitute for backup or every form of system recovery.
This guide explains how reboot-to-restore protection works, how it differs from snapshot-based rollback, and which approach may fit your environment. It also covers where Reboot Restore Standard and Enterprise fit, including centralized management for networked computers, so you can choose a practical way to reduce repeated cleanup and keep endpoints consistent.
Key Takeaways
- To freeze computer state on restart, define the approved baseline and identify which user changes should be discarded after each session.
- Match the recovery method to the need: automatic reset after restart, targeted rollback to a snapshot, or broader system restoration.
- Before deployment, map user workflows, required software, and data that must persist so protection doesn’t disrupt normal use.
- Pilot the configuration and monitor results before applying it broadly to shared Windows computers.
- Compare Reboot Restore Standard and Enterprise against your endpoint environment, and verify current edition scope and system requirements.
What Does It Mean to Freeze a Computer State on Restart?
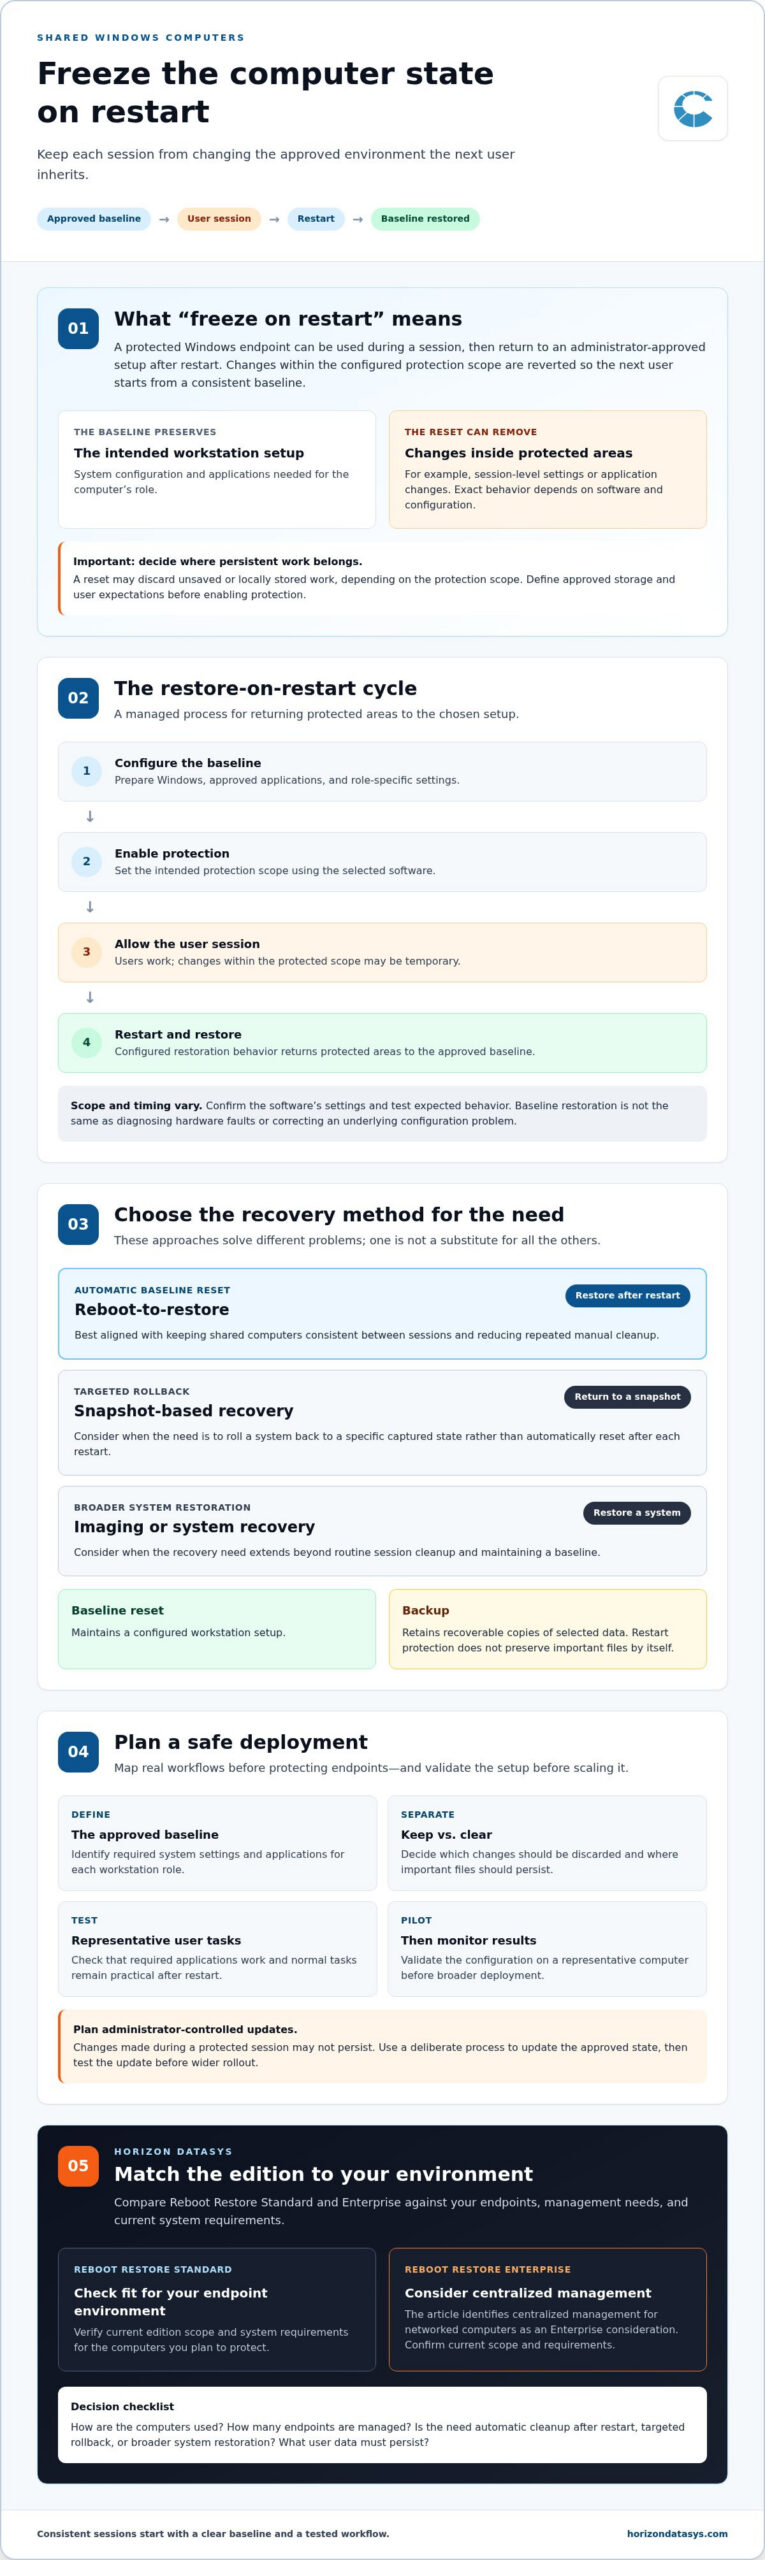
A frozen computer state isn’t a machine that refuses to change. It’s a Windows endpoint configured to return to an approved setup after it restarts. Users can work during a session, but changes within the protected scope are reverted so the next person starts from a consistent baseline.
That distinction matters on shared computers in labs, libraries, and other public-access settings, where one person’s settings or software changes shouldn’t automatically become the next person’s environment. The baseline is the approved configuration administrators want to preserve, including the system setup and applications needed for the workstation’s intended role. Before enabling protection, decide where users should save files they need to keep. A reset can remove unwanted changes, but it can also discard unsaved or locally stored work, depending on the configured protection scope.
Reboot to restore software describes this general approach: restore a computer to a defined state after a restart. The key isn’t that every computer behaves identically. Administrators choose what the protection should cover and plan the user workflow around it.
What changes are reverted when the computer restarts?
Depending on the software and its configuration, reset targets may include temporary settings, application changes, and session-level adjustments. For example, a public workstation might discard a changed desktop preference or an application configuration altered during a session. Exact behavior varies, so confirm what is protected rather than assume every file or setting is treated the same way.
Separate changes users are expected to keep from those administrators intend to clear. A required document or other persistent work needs an approved place and process to remain available; temporary downloads or session customizations may be appropriate to remove. Define these expectations before deployment and test them with representative user tasks.
How is freezing a state different from a backup?
A baseline reset returns an endpoint to a defined configuration. A backup, by contrast, retains recoverable copies of selected data so they can be restored when needed. The purposes differ: one maintains a consistent workstation setup, while the other supports data recovery. Restart-based protection shouldn’t be treated as a way to preserve important files.
An endpoint reset restores a configured computer baseline; a backup preserves recoverable copies of data. Both may have a role in an organization, but one doesn’t replace the other. A sound plan accounts for the desired workstation state and separately identifies how essential user data will be retained.
How Does Restore-on-Restart Protection Keep a Windows Baseline Consistent?
Restore-on-restart protection follows a managed cycle. An administrator prepares an approved Windows configuration, enables protection, and makes the computer available for regular sessions. When the computer restarts, the software applies its configured restoration behavior during or after the restart, returning protected areas to the approved baseline. The exact timing and scope depend on the software and its settings.
Baseline configured → Protection enabled → User session → Restart → Restored baseline
This cycle helps freeze computer state on restart and reduce repeated manual cleanup. It doesn’t diagnose every system fault or explain why a problem occurred. If an endpoint has a hardware issue or an underlying configuration problem, restoring its baseline isn’t the same as identifying or resolving the cause.
How administrators establish and update the protected baseline
Start by preparing Windows for its intended role. Install approved applications, apply the configurations users need, and confirm the workstation behaves as expected. Then enable protection according to the selected software’s setup process. For planned changes, use an administrator-controlled workflow to update the approved state rather than assuming changes made during a protected session will persist.
Test each update on a representative computer before deploying it more broadly. Check that required applications still work, the expected baseline returns after restart, and routine tasks remain practical. A controlled update process makes changes more predictable and avoids treating every workstation as a separate cleanup project.
What happens to user files and settings after restart?
Changes within the reset scope may not persist after restart. That can include user settings or files stored in protected areas, depending on the software’s configuration. Don’t promise that a particular folder, profile, or storage location will retain data unless that behavior has been verified for the specific product and setup. Tell users where to save work, and confirm any approved retention workflow through testing.
Reset scope and data-retention needs must be planned together. Define what should return to baseline and what users must be able to keep before enabling protection. Restart-based restoration maintains a configured endpoint state; it isn’t a backup strategy. For comparison, PCMag defines a system image as a copy of a drive, a distinct approach to system restoration.
For shared Windows computers that need automatic baseline restoration, review Windows endpoint restoration options and verify current product requirements and configured behavior before deployment.
Reboot-to-Restore, Snapshots, or Imaging: Which Method Fits?
The right approach depends on what should trigger restoration and how much control administrators need over the recovery point. If the goal is to freeze computer state on restart, reboot-to-restore protection is designed to automatically return protected areas to a configured baseline after each restart. Snapshots and system images address different recovery and deployment needs, so choose based on the endpoint’s operating workflow.
| Method | Trigger | Restoration scope | Typical use | Administrative workflow |
|---|---|---|---|---|
| Reboot-to-restore | Computer restarts | Configured protected areas return to the approved baseline | Shared endpoints where sessions shouldn’t permanently change the setup | Set and maintain the baseline; protection applies the reset behavior on restart |
| Snapshots | Administrator selects a recovery state | Reverts the system to a selected captured state | Recovering from a system issue while choosing when to roll back | Capture and manage recovery points, then initiate rollback as needed |
| Imaging | Deployment or a planned rebuild | Reapplies a defined computer setup | Provisioning or rebuilding endpoints to a known configuration | Maintain the image and use it as part of a deployment or recovery process |
When does automatic restore on restart make sense?
This approach fits shared computers in labs, libraries, and other public-access environments where each session should leave the next user with a consistent setup. Automatic restoration can reduce the need for staff to manually undo routine session changes. For practical deployment considerations, see this guide to automating workstation restore on reboot.
When are snapshots or traditional images a better fit?
Snapshots are useful when administrators need to select a recovery point rather than reset a computer after every restart. RollBack Rx Professional and RollBack Rx Server Edition use sector-level snapshots for system rollback, not automatic session cleanup. Imaging can support provisioning or rebuilding a defined setup. Neither method is universally better; choose based on the recovery goal and the workflow your team can maintain.
For example, a public workstation that should reset after every session has a different operating requirement from a computer that needs rollback only after a system problem. A deployment plan may also use imaging to establish a setup, then apply restart-based protection to maintain its baseline. These methods can serve distinct roles, but restart-based protection doesn’t replace data backups. Assess what needs to reset, what must remain recoverable, and how administrators will carry out each process.
How to Plan a Safe Freeze-on-Restart Deployment
A controlled rollout starts with the user workflow, not the protection setting. Before you freeze computer state on restart, determine which endpoints need a predictable baseline, what users need to do during a session, and which changes or data must persist. Then validate the setup on a limited group before expanding deployment.
- Define the use case. Identify the computers that should return to an approved state after restart, who uses them, and what each session requires. Confirm that automatic restoration fits the workflow.
- Inventory applications and changes. Record the approved applications, security settings, and user-facing configurations. Include routine system changes, such as updates, that administrators will need to apply through an approved baseline-update process.
- Plan data retention and user expectations. Identify files or records that must remain available, and verify the supported retention method for the specific product and configuration. Tell users which session changes are cleared and where work should be saved.
- Pilot and validate. Apply protection to a limited, representative group. Test normal restarts, planned updates, and typical user sessions, then compare the results with documented expectations.
- Document and monitor. Record how administrators make approved baseline changes, handle exceptions, and check that protected computers continue to behave as expected. Review the process when applications or user workflows change.
Prepare the baseline and identify data-retention requirements
Before protection is enabled, confirm that each pilot computer has the applications, security settings, and user-facing configuration its role requires. Don’t assume files or settings will persist simply because they appear available during a session. Verify retention behavior in the actual setup, and make the approved process clear to users before their first session.
Pilot, validate, and manage protected computers
Use the pilot to test more than a routine restart. Include a planned update and representative user activity, then verify that the computer returns to the intended baseline and that administrators can apply approved changes. Record exceptions or unexpected results and adjust the configuration before expanding it. For related guidance, see wiping a computer on restart safely.
A documented process makes ongoing administration more consistent. If you’re evaluating protection across networked computers, consider whether centralized management would help administrators oversee the deployment. Explore centralized management options to assess whether they fit your environment.
Choosing Horizon DataSys Software for Restart-Based Computer Protection
The right Horizon DataSys option depends on whether you need automatic cleanup at each restart or selective recovery to a chosen system state. For organizations looking to freeze computer state on restart, Reboot Restore Standard and Reboot Restore Enterprise are designed to return computers to a clean baseline. Confirm each edition’s current scope, system requirements, and licensing details before choosing.
When should administrators evaluate Reboot Restore?
Reboot Restore Standard may suit an individual Windows computer or a smaller shared-computer setup where sessions should return to the same approved baseline after restart. For a network environment where administrators need centralized management across protected computers, Reboot Restore Enterprise is the relevant option. Assess how many endpoints need consistent settings, how administrators will maintain the baseline, and whether users’ workflows fit the reset behavior before selecting an edition.
For a closer look at the enterprise option, review the Reboot Restore Enterprise evaluation guide. Use it alongside verification of current edition features and requirements for your environment.
How does RollBack Rx differ from reboot-to-restore protection?
RollBack Rx Professional and RollBack Rx Server Edition use sector-level snapshots for system recovery. This technology operates below the Windows operating system and allows administrators to roll a system back to a selected captured state. It serves a different purpose from automatic restart cleanup: rollback is an action taken to recover from a system issue, not a reset that occurs after every user session.
Use this decision summary to narrow the fit:
- Reboot Restore Standard: Evaluate for an individual or smaller shared-computer environment that needs baseline restoration on restart. Confirm current edition scope.
- Reboot Restore Enterprise: Consider when centralized management across networked computers is a requirement.
- RollBack Rx Professional or Server Edition: Consider when the need is snapshot-based system rollback to a selected recovery state rather than automatic session cleanup.
These options address different endpoint workflows, and reset-on-restart protection doesn’t replace a backup strategy. Define the restoration goal first, then verify the product’s current features and requirements against the computers and data involved. Explore Horizon DataSys endpoint protection options to assess which category fits your environment.
Choose a Baseline Strategy That Fits Your Environment
To freeze computer state on restart, first decide which changes should be cleared, what users need to retain, and how administrators will maintain the approved configuration. Restore-on-restart protection suits shared computers that should return to a consistent baseline after each session. Snapshots serve a different purpose: they let administrators roll a system back to a selected recovery state, while imaging can support deployment or rebuilding.
Reboot Restore returns shared computers to a clean baseline on restart. For network environments, Reboot Restore Enterprise adds centralized management tools to help administrators coordinate protected computers. Whatever approach you choose, test the configuration with real workflows and keep data-retention and backup plans separate from endpoint reset behavior.
A clear deployment plan can reduce repeated manual cleanup while keeping the user experience predictable. Evaluate Horizon DataSys restore-on-restart solutions to assess which option aligns with your endpoints and management needs. With the right fit and a validated baseline, your team can maintain a more consistent computing environment.
Frequently Asked Questions
Can I freeze a Windows computer so it returns to the same state after every restart?
Yes. Reboot-to-restore software can return a Windows computer to a configured baseline after it restarts. Reboot Restore Standard and Reboot Restore Enterprise are designed to restore shared computers to a clean baseline on restart. The exact protected areas and behavior depend on the product configuration, so test the setup and confirm what users can change or retain before deploying it broadly.
What does freeze computer state on restart mean?
To freeze computer state on restart means configuring software to revert protected changes when a computer restarts, rather than preventing users from making changes during a session. The baseline is the approved configuration the computer returns to, including the setup and applications required for its role. Administrators define and maintain that state, while the software applies its configured restoration behavior after restart.
Will freezing a computer on restart delete files and settings?
Files and settings within the configured reset scope may not persist after restart. The result depends on the software, its protection settings, and where information is stored, so don’t assume a file or profile will be retained without testing. Before enabling protection, identify what users need to keep, verify the supported retention method, and tell users where to save work that must remain available.
Is restore-on-restart software the same as a backup?
No. Restore-on-restart software returns protected parts of a computer to a defined baseline; a backup retains recoverable copies of data for restoration when needed. These methods serve different purposes. Resetting a workstation can help keep its setup consistent, but it shouldn’t be relied on to preserve important user files or replace a backup plan. Plan endpoint restoration and data retention separately.
How is reboot-to-restore different from a system snapshot?
Reboot-to-restore automatically returns protected areas to a baseline after each restart. A snapshot captures a system state that an administrator can select when rollback is needed. Horizon DataSys’s RollBack Rx Professional and RollBack Rx Server Edition use sector-level snapshots for system rollback, not automatic cleanup after every session. Choose based on whether you need a routine reset or recovery to a selected state.
Can administrators update the protected computer baseline?
Yes. Administrators can plan changes to the approved setup, such as updating required applications or configurations, and apply them through the product’s supported baseline-management workflow. Don’t assume changes made during an ordinary protected session will become permanent. Test planned changes on a representative computer, verify the result after restart, and document the steps for applying updates consistently across protected endpoints.
Is Reboot Restore suitable for shared computers?
Reboot Restore is designed for shared computers that need to return to a clean baseline on restart, making it a potential fit for public-access workstations, libraries, and labs. Reboot Restore Standard may suit an individual or smaller shared-computer setup, while Reboot Restore Enterprise adds centralized management tools for network environments. Check current edition scope, system requirements, and data-retention needs before selecting an option.